

Condixia – REST Gateway
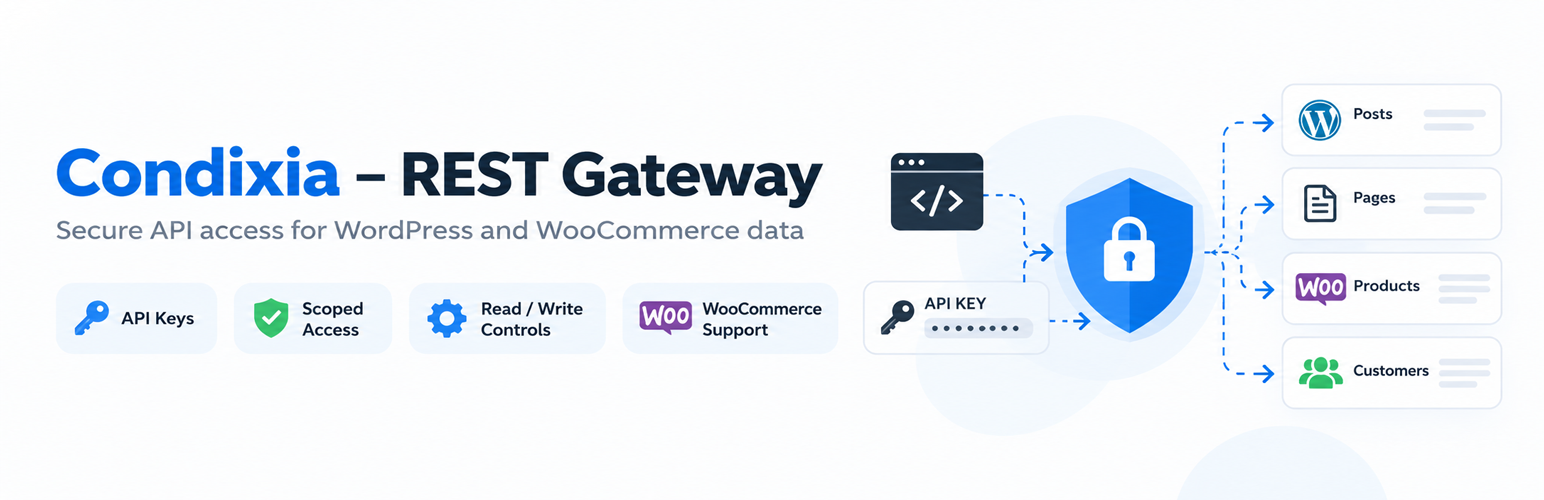
Condixia – REST Gateway provides authenticated and controlled REST access to WordPress content and selected WooCommerce data for external applications.
It is designed for developers building applications such as Laravel dashboards, headless frontends, mobile applications, internal tools, reporting systems, and SaaS integrations that use WordPress as a backend.
Condixia uses its own API client and credential system. External applications do not need WordPress user passwords, login cookies, Application Passwords, WooCommerce consumer keys, JWT plugins, or OAuth plugins.
Core Features
- Secure Condixia API clients and Bearer credentials.
- API credentials are stored as hashes rather than reusable plaintext secrets.
- API secrets are displayed only when initially created.
- Per-client scopes and permissions.
- Credential expiration, disabling, and revocation.
- Versioned REST namespace using
condixia/v1. - Read access to posts, pages, and supported public custom post types.
- Explicitly controlled create and update access for supported WordPress content.
- Write operations are disabled by default per resource.
- Read-only WooCommerce product access.
- Read-only WooCommerce order access.
- WooCommerce HPOS-compatible order access using supported WooCommerce APIs.
- Pagination, searching, filtering, sorting, and field selection where supported.
- Basic per-client rate protection.
- Resource schemas that prevent unrestricted field and metadata exposure.
- Endpoints documentation inside WordPress Admin.
- API client management inside WordPress Admin.
- No DELETE operations in the Free edition.
Security Model
Condixia separates authentication from authorization.
Authentication determines which Condixia API Client is making the request.
Authorization determines which resources and operations that client may access.
Successfully authenticating does not automatically grant unrestricted access.
Resources expose explicitly defined fields rather than raw WordPress or WooCommerce objects. Arbitrary post metadata, authentication data, session information, API secrets, and other protected internal values are not exposed by default.
WordPress content writes use supported WordPress APIs. WooCommerce order and product access uses supported WooCommerce APIs.
Authentication
External applications authenticate using an HTTP Bearer credential:
Authorization: Bearer cxi_v1_<client-id>.<secret>
The plaintext secret is shown only when the API client is created.
Store API credentials securely in your external application.
Production API requests should use HTTPS.
Example Request
Retrieve WordPress posts:
GET /wp-json/condixia/v1/resources/posts
Example cURL request:
curl -H "Authorization: Bearer <your-api-key>" "https://example.com/wp-json/condixia/v1/resources/posts"
Retrieve a specific post:
GET /wp-json/condixia/v1/resources/posts/123
Retrieve WooCommerce products:
GET /wp-json/condixia/v1/resources/products
Retrieve WooCommerce orders:
GET /wp-json/condixia/v1/resources/orders
Available resources depend on the active WordPress post types, installed plugins, WooCommerce availability, resource configuration, and the API client’s assigned scopes.
Third-Party Libraries
Condixia – REST Gateway includes Select2 for searchable multi-select controls in the WordPress administration interface.
Select2
Version: 4.1.0
License: MIT
Project: https://select2.org/
Source: https://github.com/select2/select2
The Select2 license is included with the bundled library.
Details


Related plugins
Plugins that also contain the tag api
WP Consent API
InfiniteWP Client
Disable REST API
Disable WP REST API
WordPress REST API (Version 2)
WP REST Cache

About
Plugin for that tries to help you find the WordPress plugin you are looking for.
| Please enjoy an image of Crush (this awesome turtle) and have a lovely day! |  |
We do not own any plugin listed on this site and do not work for or work with WordPress.com or it's associated companies. We simply provide a searchable list of the available WordPress plugins.