

Consiva.ai
Consiva.ai scans your site for the cookies and trackers it really uses, blocks them until visitors agree, and re-scans your site each time you activate or change your consent settings.
Every consent decision becomes a timestamped, versioned, tamper-evident record you can export from your Consiva dashboard. You can see which notice version a visitor read, which purposes they allowed, and which configuration was in force at that moment.
Consiva.ai helps businesses implement privacy and consent controls, and helps you work toward DPDP-aligned and GDPR-aligned privacy practices.
What this plugin does
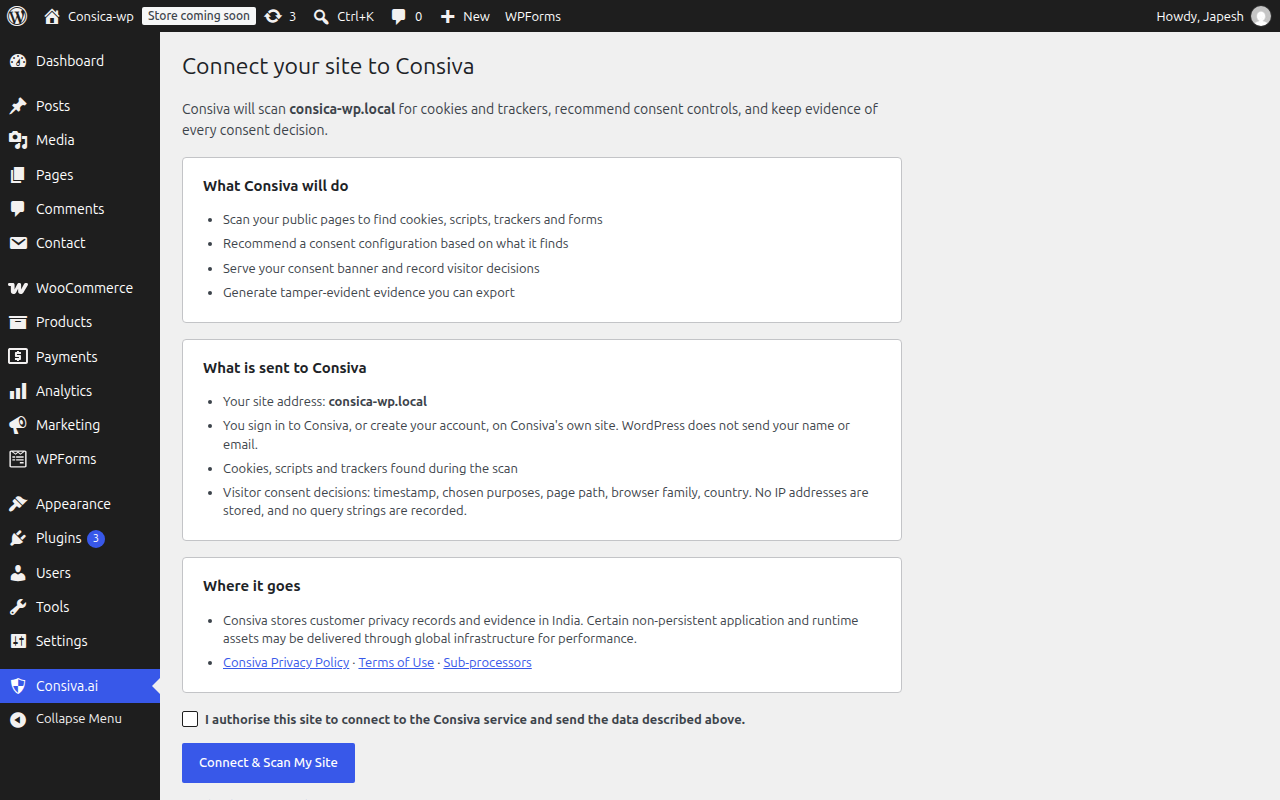
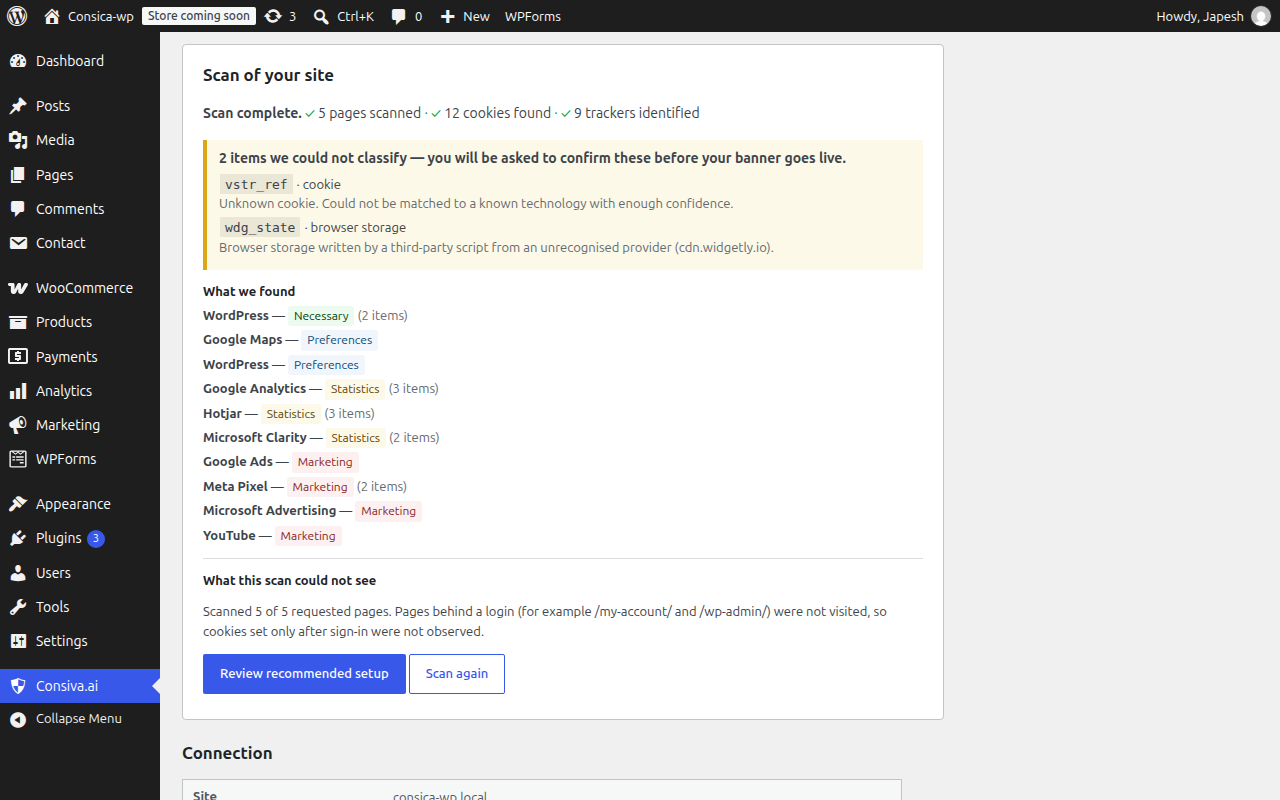
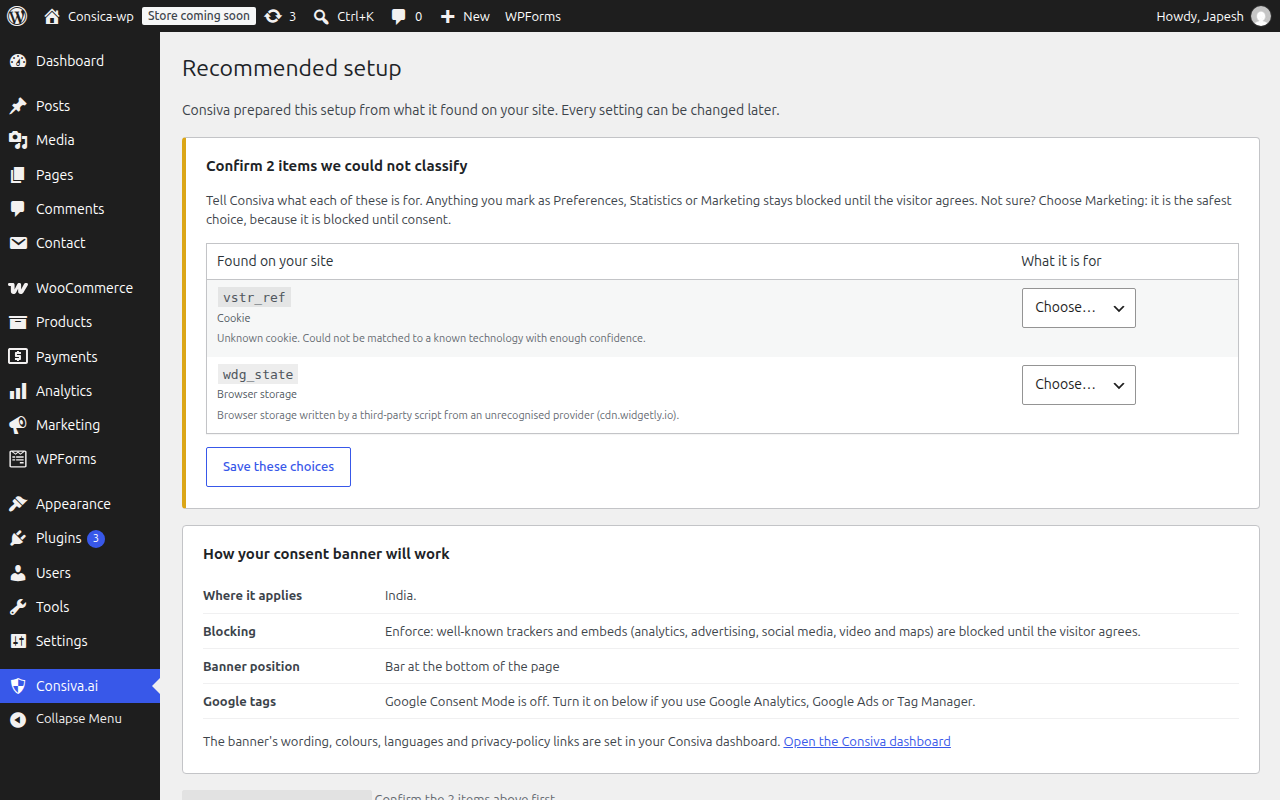
- Scans your public pages for cookies, scripts, trackers, forms and embeds, and tells you plainly what it could not reach.
- Prepares a recommended setup and asks you to confirm anything it could not classify.
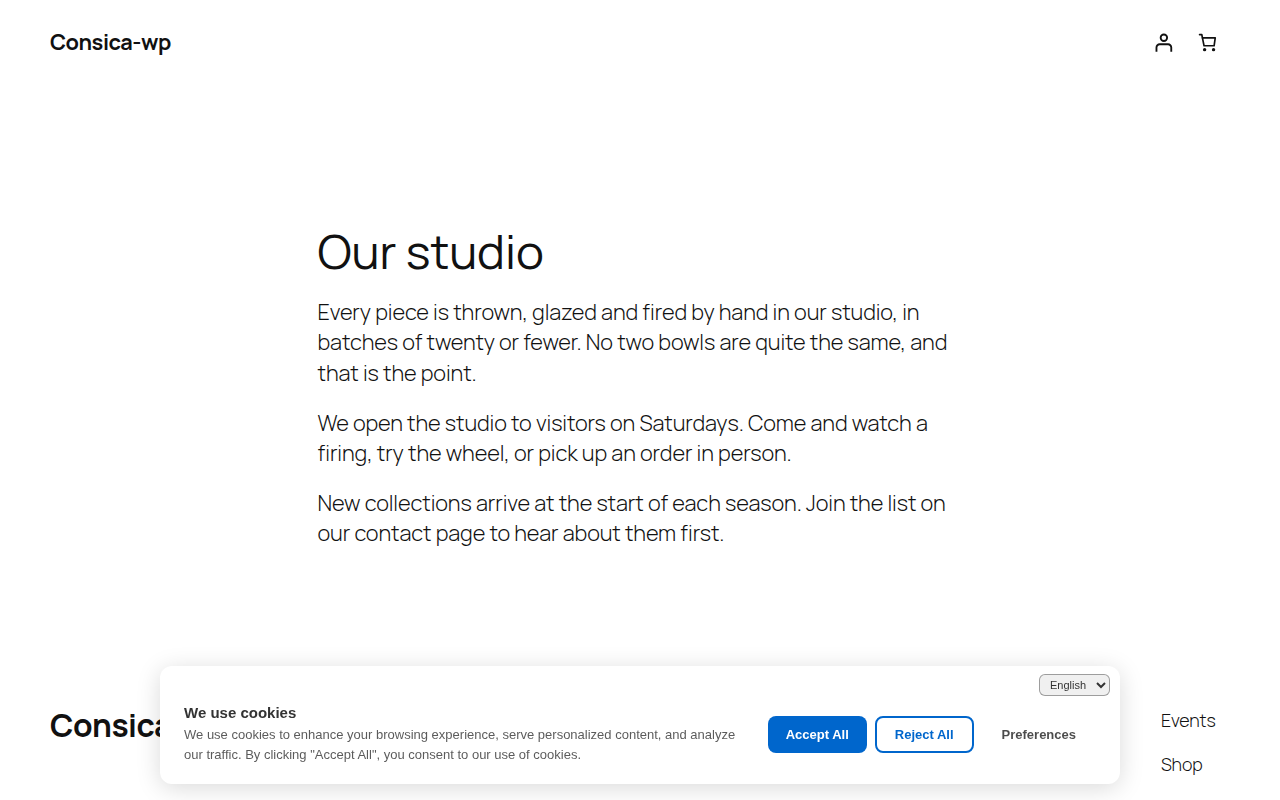
- Serves Consiva’s banner and preference centre. Its wording, colours and languages are set in your Consiva dashboard.
- Blocks well-known tracking scripts and embeds (analytics, advertising, social media, video and maps) until a visitor consents: scripts added the WordPress way, tags written into your theme (on WordPress 6.9 or later), and trackers that other scripts add later.
- Optionally signals Google Consent Mode v2 to your Google tags.
- Records every decision and withdrawal, with evidence you can export from your Consiva dashboard.
- Re-scans your site after every change to your consent settings, and tells you honestly where it cannot help.
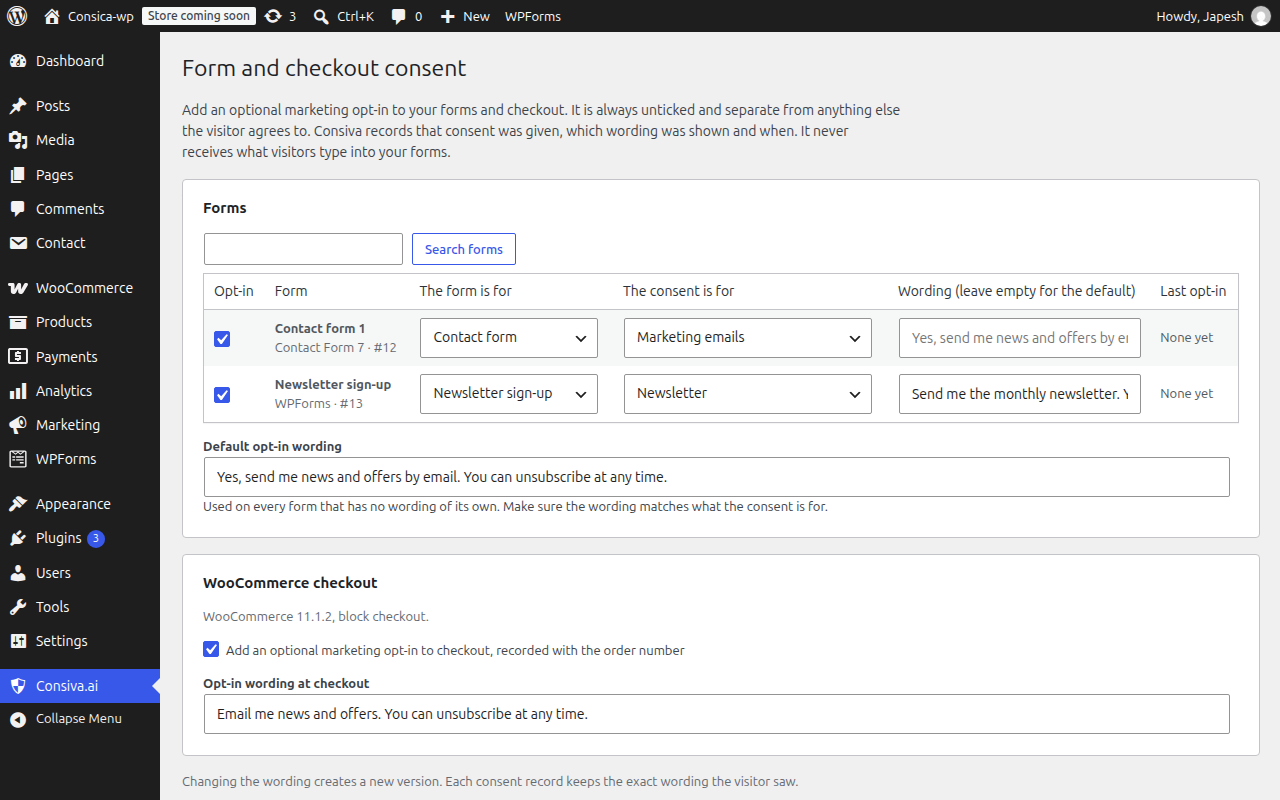
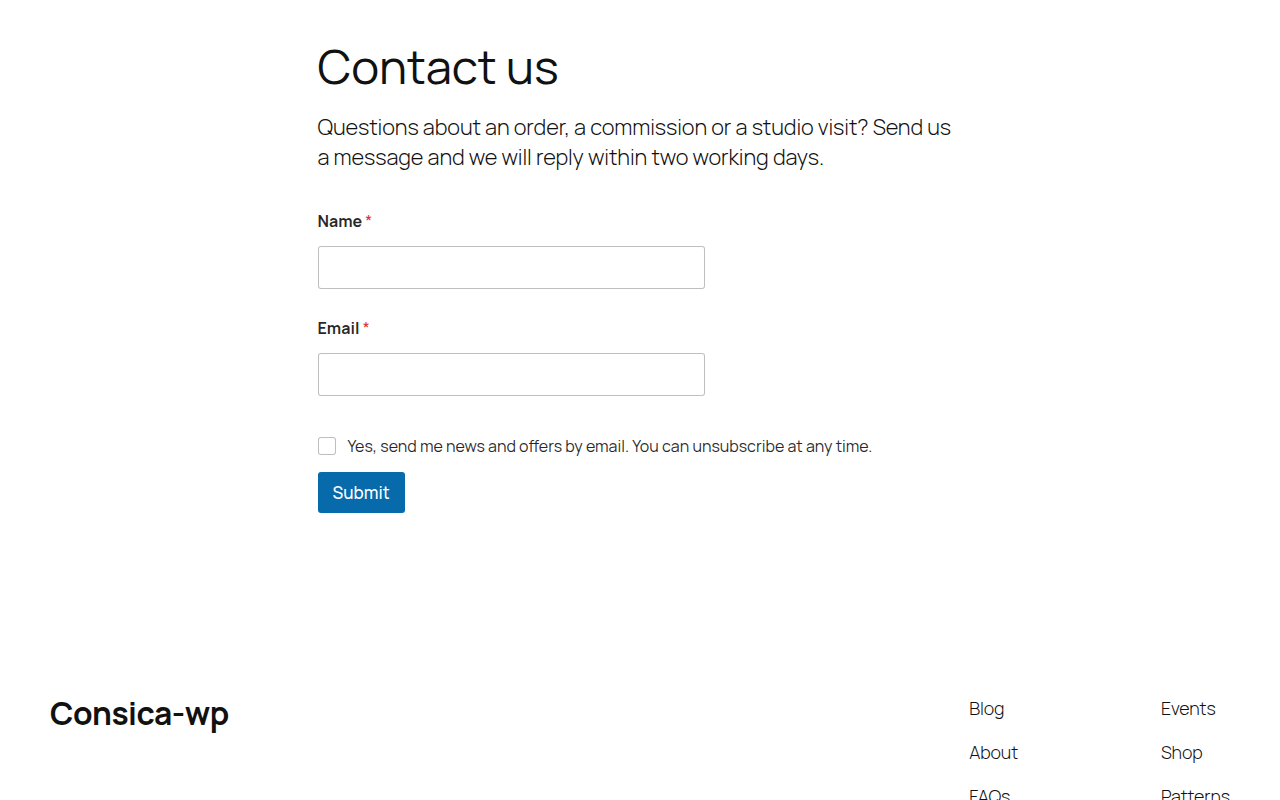
- Detects WooCommerce and adds an optional, unticked marketing opt-in at checkout.
- Captures marketing consent on Contact Form 7 and WPForms forms.
- Suggests text for your privacy policy.
- Works on multisite: each site connects and is configured separately; network admins get a read-only overview.
Five key benefits
- See what’s actually on your site. An automatic scan finds cookies, trackers, forms and embeds, and tells you plainly what it could not reach.
- Go live in minutes, not an afternoon. A recommended configuration and one click to activate. No keys, no code, no theme editing.
- Know what is on your site. Consiva re-scans your site whenever you change your consent settings.
- Keep evidence you can hand to an auditor. Tamper-evident, versioned records of every decision, exportable from your Consiva dashboard.
- Grow into privacy operations. Start with consent; add rights requests, breach records and processor governance in Consiva when you need them.
What it does not do
No plugin or service can make a website legally compliant, and this one does not claim to. Consiva.ai helps you implement privacy and consent controls, and helps you keep evidence of them. Responsibility for your site’s compliance remains with you.
Consiva cannot block tags that run on your server, inline code snippets it does not recognise, or third-party cookies once a script has run. The verification scan tells you when something still fires before consent, and where.
Performance
Pages never wait for Consiva: the front end reads only settings already stored on your site, and the plugin adds no database queries. Measured on a test site: about 2–3 ms of added PHP time per page, a 1.4 KB inline script (1.6 KB with Google Consent Mode on, gzipped), and no layout shift. On a visitor’s first page view, Consiva’s banner is often the largest thing painted, so speed tools may report a later Largest Contentful Paint while it appears; your page’s own content is not held back.
Accessibility
The plugin’s own admin screens are tested against WCAG 2.1 AA, work with the keyboard alone, reflow at 400 % zoom, respect reduced motion, and support right-to-left languages. The visitor-facing banner is Consiva’s, and its accessibility is Consiva’s to state.
Source code
The plugin’s admin JavaScript and CSS ship as readable source; there is no build step.
One script is minified by hand: the small inline script the plugin prints first on every page (it holds back trackers until the visitor chooses), kept short so it does not slow pages down. Its readable source, with full names and comments, is included at assets/src/consent-bootstrap.js. It is not loaded; the plugin’s tests run every scenario against both versions so they stay identical.
External services
This plugin is an interface to the Consiva privacy service, operated by Swaran Soft Support Solutions Pvt. Ltd. Scanning, classification, consent records, evidence generation and verification happen on Consiva’s servers. Nothing is sent to Consiva until you explicitly authorise the connection on the plugin’s Get Started screen: activating the plugin makes no outbound requests.
Consiva stores customer privacy records and evidence in India. Certain non-persistent application and runtime assets may be delivered through global infrastructure for performance.
- Terms of Service: https://consiva.ai/legal/terms-of-service
- Privacy Policy: https://consiva.ai/legal/privacy-policy
- Sub-processors: https://consiva.ai/legal/privacy-policy#subprocessors
What is sent, and when:
- When you connect (you tick the authorisation box and choose Connect): your browser goes to app.consiva.ai to sign in or create your Consiva account. Your site then sends api.consiva.ai its domain, the connection code, and WordPress as the platform. Consiva briefly fetches one address on your site (
/?consiva-verify=…) to confirm you control the domain. - While connected (from your site’s server to api.consiva.ai): requests to start and follow scans, read results and your consent settings, apply the settings you choose, and a daily connection check. Consiva’s scanner visits your public pages, as a visitor would.
- On your visitors’ pages: their browser loads Consiva’s banner script from api.consiva.ai, reads your published banner settings from there, and sends each consent decision there: the choices made, a random visitor ID, the page address, the language and the notice version. As with any web request, Consiva’s servers receive the visitor’s IP address and browser details. The choice is kept in the visitor’s browser storage (
cmp_consent, andcmp_visitor_id), or in cookies of the same names if that storage is blocked. - Form and checkout opt-ins (only on forms you enable): your site sends api.consiva.ai that a visitor agreed to the opt-in’s purpose (such as marketing emails or a newsletter), when, the kind of form, the form’s name, the page address (without query string), the exact wording of the checkbox and, for checkout, the order number. Never names, email addresses or other form contents.
- When you delete the plugin: Consiva is told to revoke this site’s credentials and pause the banner; your account, consent records and evidence are kept.
Tracker addresses in the plugin: the plugin contains a list of well-known tracker addresses (Google Tag Manager, Google Analytics, Google Ads, Meta, Hotjar, Microsoft Clarity, Heap, Clicky, LinkedIn, TikTok, HubSpot, Microsoft Advertising, X, YouTube, Vimeo and Google Maps) so it can recognise those scripts and embeds on your pages and hold them back until the visitor consents. The plugin never contacts these services and sends them nothing; they are only loaded if your site already includes them and the visitor agrees.
A free plan is available. Paid plans are for additional service capability and are purchased at app.consiva.ai. All plugin code is fully available under GPLv2 or later; nothing in the plugin is locked.
Details

Related plugins
Plugins that also contain the tag consent-management
Consent Mode Banner
Concord – Cookie Banner & Full Privacy Platform for Cookie Consent & GDPR/CCPA Compliance

QookieQloud™ Consent Management

BigID Consent Management Platform

PrivacyTech CMP
Biskoui

About
Plugin for that tries to help you find the WordPress plugin you are looking for.
| Please enjoy an image of Crush (this awesome turtle) and have a lovely day! |  |
We do not own any plugin listed on this site and do not work for or work with WordPress.com or it's associated companies. We simply provide a searchable list of the available WordPress plugins.