

DevaGroup DevaGuard – Site Security Monitor
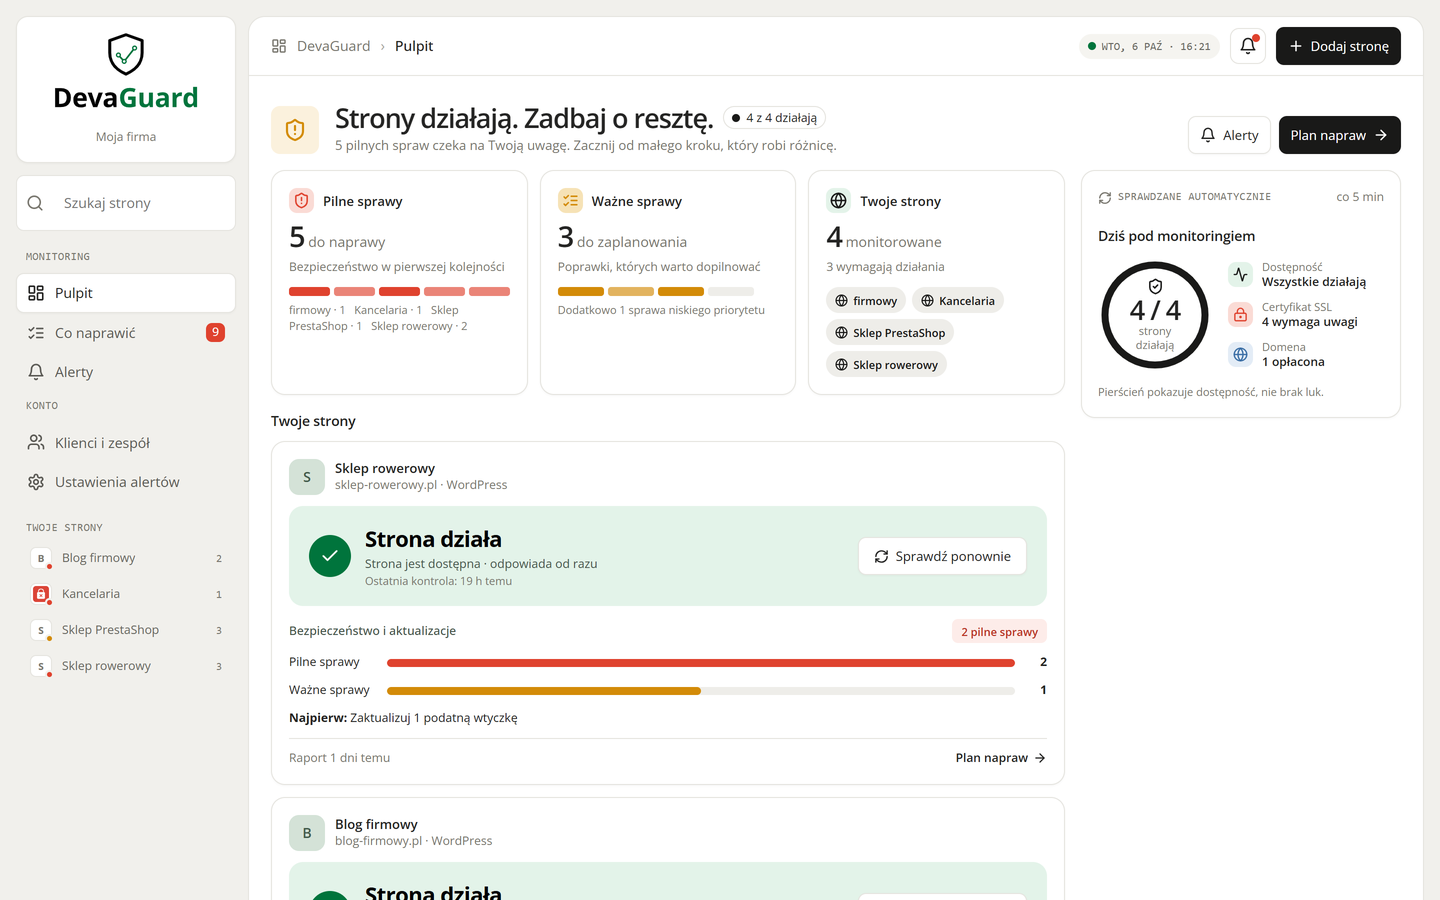
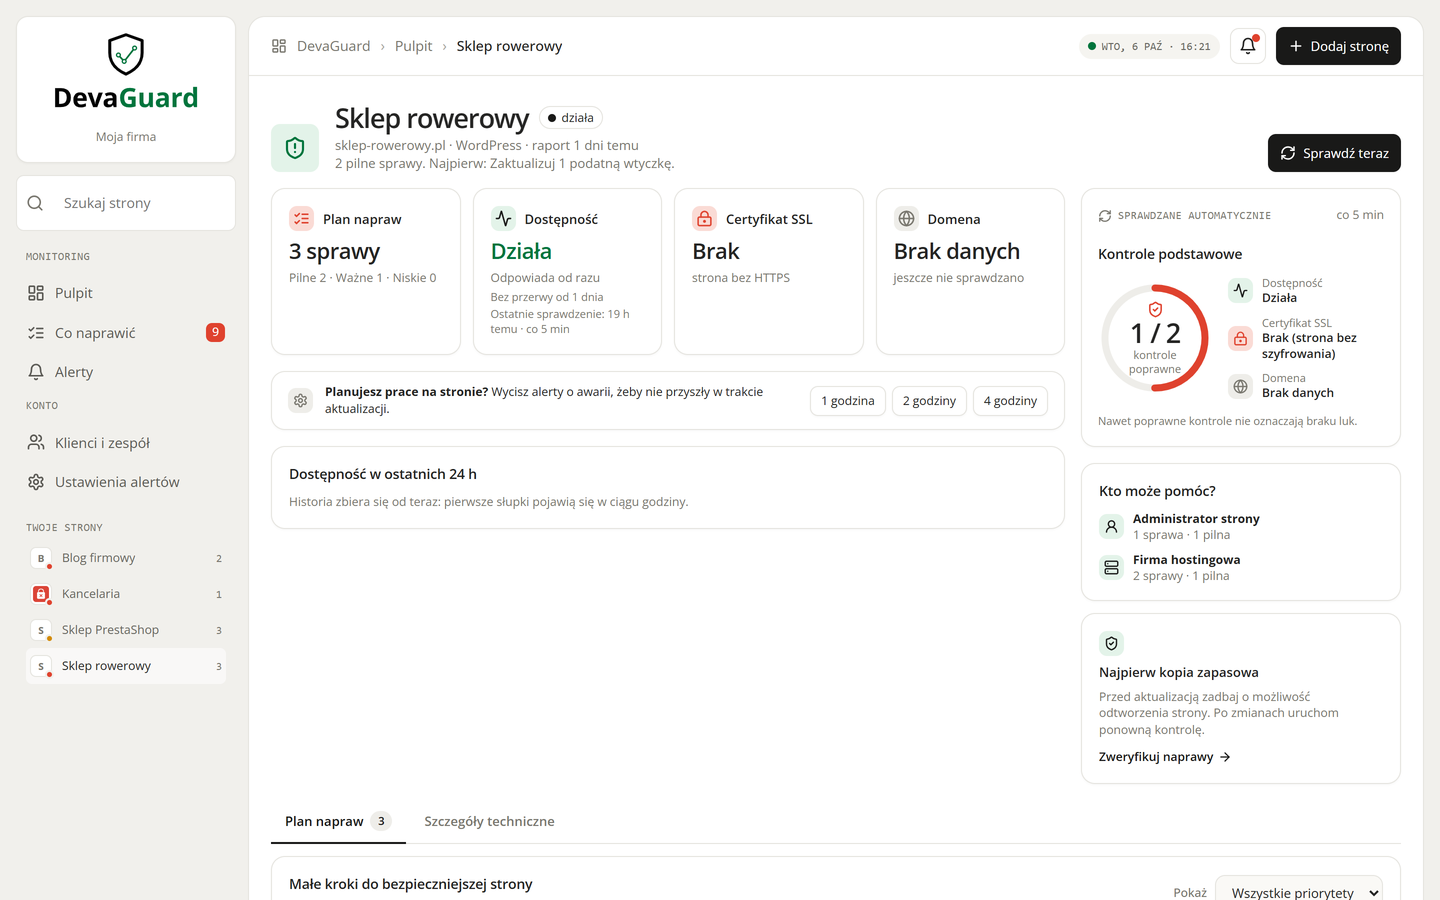
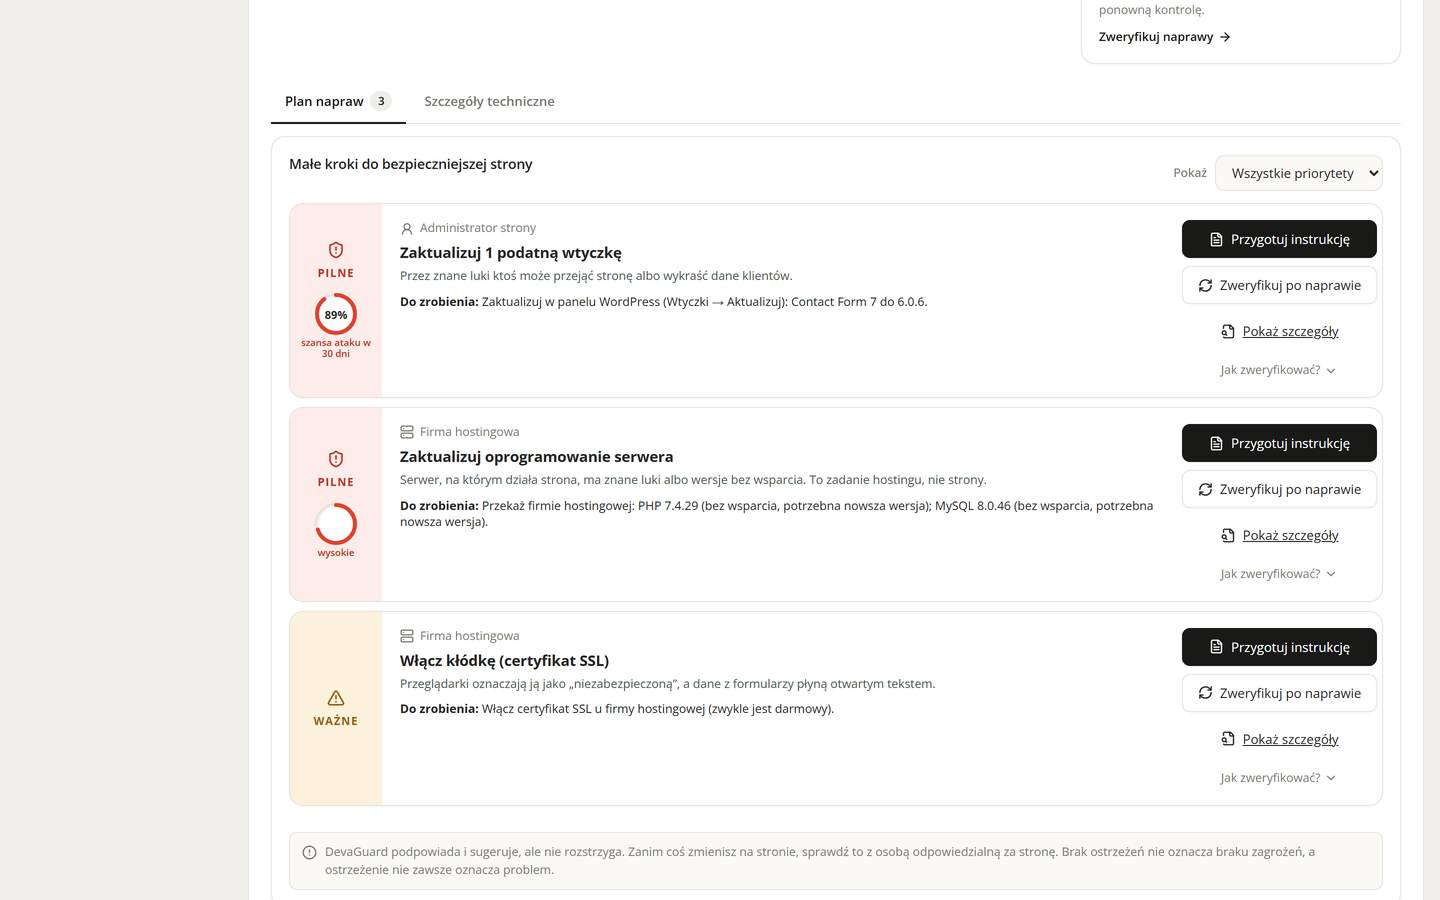
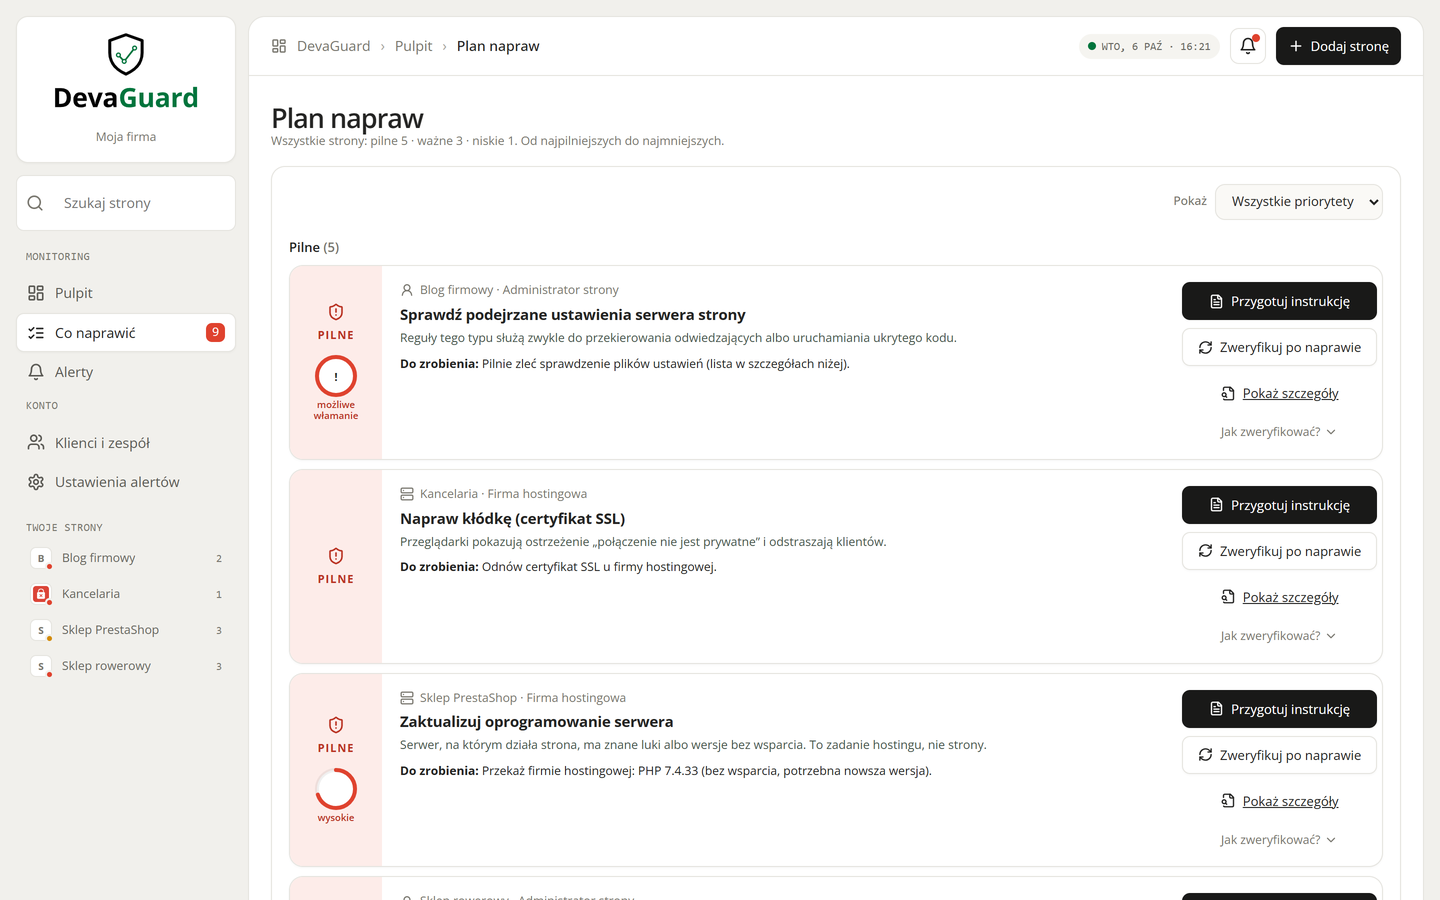
DevaGuard is a website security monitoring service run by DEVAGROUP sp. z o.o., Kraków, Poland. This plugin connects your site to a DevaGuard dashboard. Once a day, and right after every update, it collects information about your site and sends it to the DevaGuard server you configure. The dashboard turns it into a plain-language repair plan: what is urgent, why it matters and who should fix it.
The plugin is read-only. It never changes your content, settings or files, never installs anything and does not expose any endpoint on your site.
What the plugin reports:
- WordPress, PHP, database and web server versions, plugins and themes with available updates.
- File integrity: core and WordPress.org plugin files compared with official checksums, PHP files in uploads, unknown PHP files in wp-content, files changed in the last 7 days.
- Suspicious rules in .htaccess, .user.ini and wp-config.php (only findings and a file hash are sent, never the file contents).
- Injected scripts in posts, options and post meta (only the location and type of finding are sent, never the content).
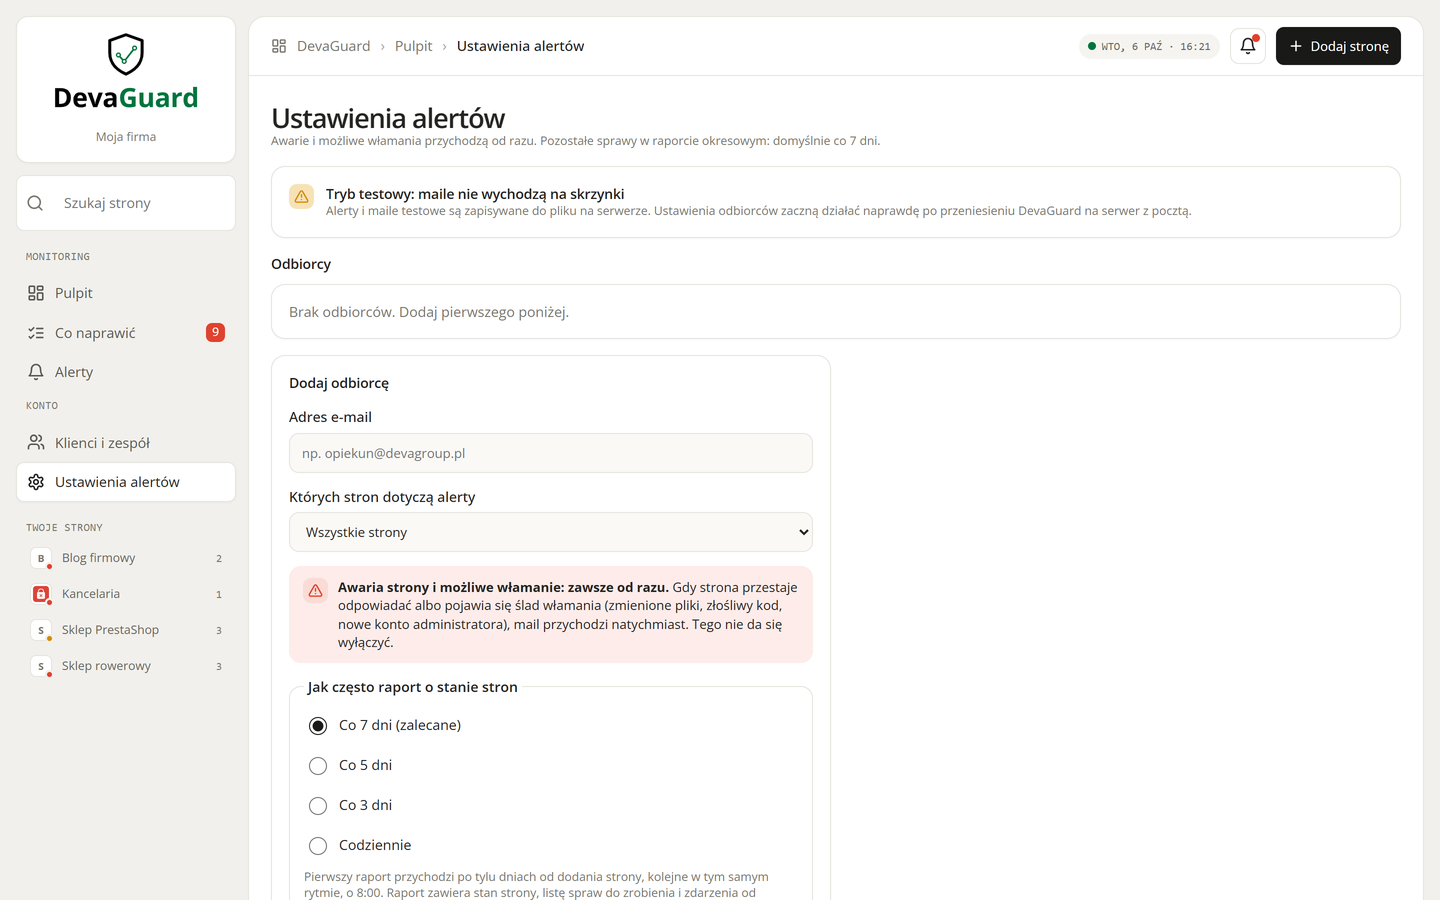
- Administrator events: new administrator, e-mail or password change, login from a new network, failed login bursts. Logins and IP addresses stay on your site; only hashes and counts are sent.
- Last backup date (UpdraftPlus and common backup plugins).
DevaGuard suggests what to check. It is not an oracle and does not replace the person responsible for the site or a security audit. No warnings does not mean no risk.
DevaGuard is not limited to WordPress. Sites built on PrestaShop, Joomla, Drupal, Magento, OpenCart or custom code are monitored with a single agent file or with checks from outside (uptime, SSL, domain, blacklists). This plugin is the WordPress part of the service.
DevaGuard is built and maintained by DevaGroup. Service, dashboard and help: devaguard.pl.
External services
This plugin sends data to a DevaGuard server. Nothing is sent until an administrator enters the server address and the site key in Tools DevaGuard.
- What is sent: the report described above (software versions, plugin and theme list, integrity and configuration findings, hashed administrator logins, event counts). Passwords, wp-config.php contents, post contents and visitor or administrator IP addresses are never sent.
- When: once a day, after plugin, theme or core updates, and when you click “Send data now”. In addition, every 5 minutes (WP-Cron) a short signed “site is alive” signal is sent to the same server. It contains the site ID, a timestamp, a signature, the signal interval, the HTTP status code and response time of the site’s own home page (checked by the plugin with a request to the site itself) and the expiry date of the site’s SSL certificate (read at most every 12 hours). No content of the site and no personal data. It lets the dashboard tell a real outage from a hosting firewall that blocks the DevaGuard server.
- Where: the server address you enter. The DevaGuard service is operated by DEVAGROUP sp. z o.o., Kraków, Poland.
- Terms of service: https://devaguard.pl/regulamin
- Privacy policy: https://devaguard.pl/polityka-prywatnosci
To check whether sensitive files (for example .env, wp-config.php backups or database dumps) are publicly accessible, the plugin requests those files from your own site (a request to itself, only for files that exist on disk). Only the file path and the result are reported, never the file contents. In the same way the plugin checks whether visitors can see account logins (/?author=1, /wp-json/wp/v2/users), XML-RPC, the WordPress version in the page code and readme.html; only yes/no results, the number of listed accounts and the version number are reported.
To check file integrity the plugin also downloads official checksums from WordPress.org (api.wordpress.org and downloads.wordpress.org). Only the WordPress version, locale, plugin slugs and plugin versions are sent there.
Details

Related plugins
Plugins that also contain the tag file-integrity
File Change Monitor

Malsift – Malware Scanner & Cleanup
MadTek Entrusans ™ IDS client

WebKernelAI Security

Milardovich File Modification Monitor
ice Scanner Security

About
Plugin for that tries to help you find the WordPress plugin you are looking for.
| Please enjoy an image of Crush (this awesome turtle) and have a lovely day! |  |
We do not own any plugin listed on this site and do not work for or work with WordPress.com or it's associated companies. We simply provide a searchable list of the available WordPress plugins.