

HiveKit External API Page Content
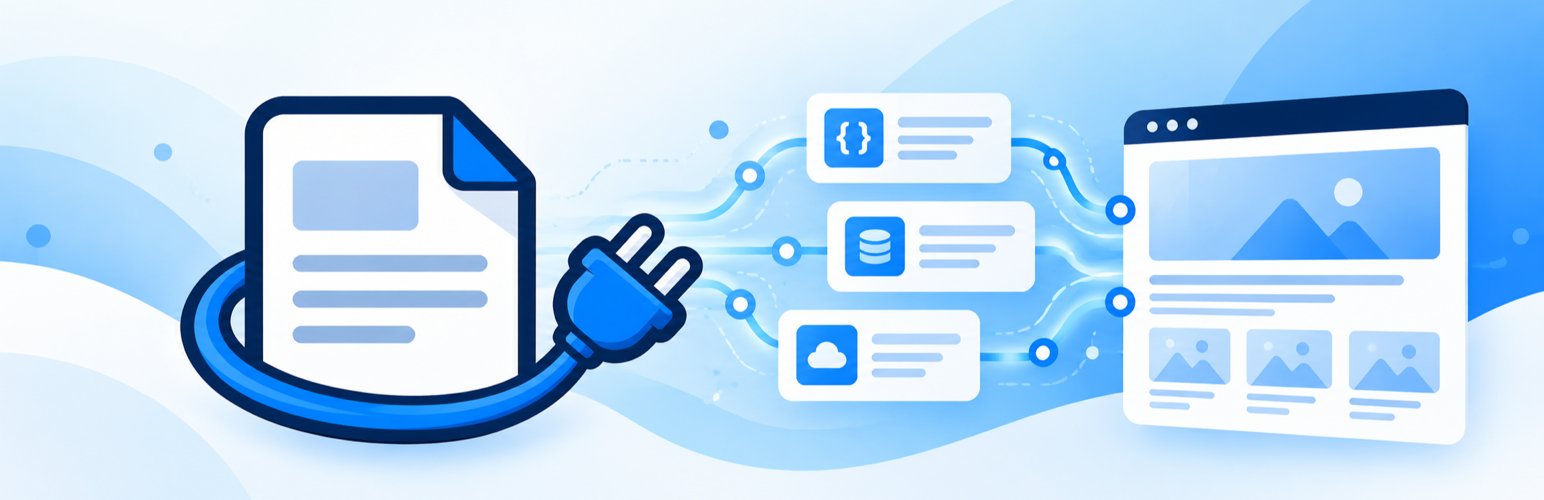
External API Page Content lets you create any number of configurable page-to-API mappings. No page purpose or endpoint is hard-coded.
Each mapping contains:
- an optional administrative label
- a WordPress page
- an external API URL
- payload format: auto-detect, HTML, or Markdown
- its own cache TTL
- optional HTTP request headers, entered one per line
- enabled/disabled status
The endpoint must return the document directly in the HTTP response body. JSON/XML wrappers are not expected.
Features:
- Repeatable mappings: add or remove as many mappings as needed.
- Uses the WordPress HTTP API (
wp_safe_remote_get). - Auto-detects HTML vs Markdown, or lets you force the format per mapping.
- Sanitizes output before rendering.
- Caches successful responses with a configurable TTL per mapping.
- Keeps the last successful API response per mapping as an outage fallback.
- Falls back to the original WordPress editor content if the API has never succeeded.
- Does not read PHP constants and does not store secrets, so it cannot be used to send
wp-config.phpvalues such as database credentials to a remote server. - Includes a per-mapping Test API button that shows the raw response payload, HTTP status, content type, size, and detected format without changing the cache.
- Supports per-mapping request headers using a simple
Header-Name: valuetextarea. - Offers filters for advanced request/header customization.
Upgrading from 1.0
Version 1.1 automatically converts the old fixed-slot settings into ordinary mappings. After migration there is no special handling for any page purpose.
Version 1.3.0 removed the per-mapping token constant setting. The plugin no longer reads any PHP constant, so an administrator account cannot use it to send wp-config.php values such as database credentials to a remote URL. If you relied on that setting, add the header with the hivekit_eapc_request_args filter (see Authentication below), or type it into the mapping’s Request headers field.
Request headers
Each mapping has a Request headers textarea. Enter one header per line:
X-API-Key: abc123
X-Tenant: customer-a
Accept-Language: en
Header names are validated and control characters are removed from values. Malformed lines are ignored. Explicit mapping headers take precedence over the plugin’s default headers when the same header name is supplied.
Header values entered here are stored in the WordPress options database, so anyone who can read the database can read them. For secrets, the filter shown under Authentication is preferable because it keeps the value in your own code.
The Test API button uses the request headers currently entered in the mapping, including unsaved changes.
Authentication
The plugin does not read PHP constants and does not store secrets. It therefore cannot be used to send a value from wp-config.php, such as DB_PASSWORD or AUTH_KEY, to a remote server.
Add an Authorization header from your own code with the hivekit_eapc_request_args filter, from a small site-specific plugin or your theme:
add_filter( 'hivekit_eapc_request_args', function( $args ) {
    $args['headers']['Authorization'] = 'Bearer ' . MY_CONTENT_API_TOKEN;
    return $args;
} );
The filter receives ( $request_args, $url, $page_id, $mapping_id, $mapping ), so a token can be limited to one mapping:
add_filter( 'hivekit_eapc_request_args', function( $args, $url, $page_id, $mapping_id, $mapping ) {
    if ( 'm2' === $mapping_id ) {
        $args['headers']['Authorization'] = 'Bearer ' . MY_LEGAL_API_TOKEN;
    }
    return $args;
}, 10, 5 );
Any other header works the same way:
add_filter( 'hivekit_eapc_request_args', function( $args, $url, $page_id, $mapping_id, $mapping ) {
    if ( 'Policy API' === $mapping['label'] ) {
        $args['headers']['X-API-Key'] = 'replace-me';
    }
    return $args;
}, 10, 5 );
The Test API button runs the same filter, so a test sends exactly the headers a real fetch would.
Cached responses are not keyed by filtered arguments, so rotating a token does not by itself refresh cached content. Clear the cache after changing a token.
Security
- URLs are restricted to public HTTP/HTTPS endpoints and fetched with
wp_safe_remote_get(). - HTML responses are sanitized using WordPress KSES rules for post content.
- Markdown is converted to HTML and sanitized before display.
- Script tags and other unsafe HTML are removed by default.
- The plugin never reads PHP constants, so it cannot expose
wp-config.phpsecrets such as database credentials or authentication salts. - Secrets are not written to the plugin settings. Values typed into a mapping’s Request headers field are stored in the site options table.
If you intentionally need additional HTML tags/attributes, use the hivekit_eapc_allowed_html filter.
Markdown support
The bundled dependency-free Markdown renderer is intentionally small and supports the common constructs typically used in content/legal documents:
- headings
- paragraphs
- blockquotes
- horizontal rules
- fenced code blocks
- ordered and unordered lists
- links
- inline code
- bold, emphasis, and strikethrough
It is not a full CommonMark implementation. If your source documents depend on advanced Markdown features such as tables, nested lists, footnotes, or reference-style links, replace/extend the renderer through the hivekit_eapc_markdown_html filter or integrate a full Markdown parser.
Filters
hivekit_eapc_should_replace_content
Controls whether content replacement occurs. Receives the page ID and full mapping.
hivekit_eapc_request_args
Changes WordPress HTTP request arguments before the API request. Receives URL, page ID, stable mapping ID, and full mapping.
hivekit_eapc_allowed_html
Changes the WordPress KSES allowlist for HTML responses.
hivekit_eapc_markdown_html
Changes rendered/sanitized Markdown HTML.
hivekit_eapc_rendered_content
Changes the final HTML before caching/output. Receives the stable mapping ID and full mapping.
External requests and privacy
This plugin does not send any data to the plugin author or to WordPress.org.
For every enabled mapping, the plugin performs a server-side HTTP request to the exact URL entered on the settings screen and replaces the body of the mapped page with the response. You choose those endpoints, so review the privacy policy and terms of use of each API you connect before enabling a mapping.
Requests use the WordPress HTTP API (wp_safe_remote_get) and accept only public HTTP/HTTPS URLs. Redirects are limited to 3, the response body is capped at 2 MB and the request times out after 8 seconds.
Source code and support
Development happens at https://github.com/corradofiore/wp-external-api-page-content
Bug reports and feature requests are welcome there. The distributed plugin contains the same unminified source as the repository, so no build step is required to review the code.
Details

Related plugins
Plugins that also contain the tag api
WP Consent API
InfiniteWP Client
Disable REST API
Disable WP REST API
WordPress REST API (Version 2)
WP REST Cache

About
Plugin for that tries to help you find the WordPress plugin you are looking for.
| Please enjoy an image of Crush (this awesome turtle) and have a lovely day! |  |
We do not own any plugin listed on this site and do not work for or work with WordPress.com or it's associated companies. We simply provide a searchable list of the available WordPress plugins.