


IPScanner – Block Bots, VPNs & Proxies
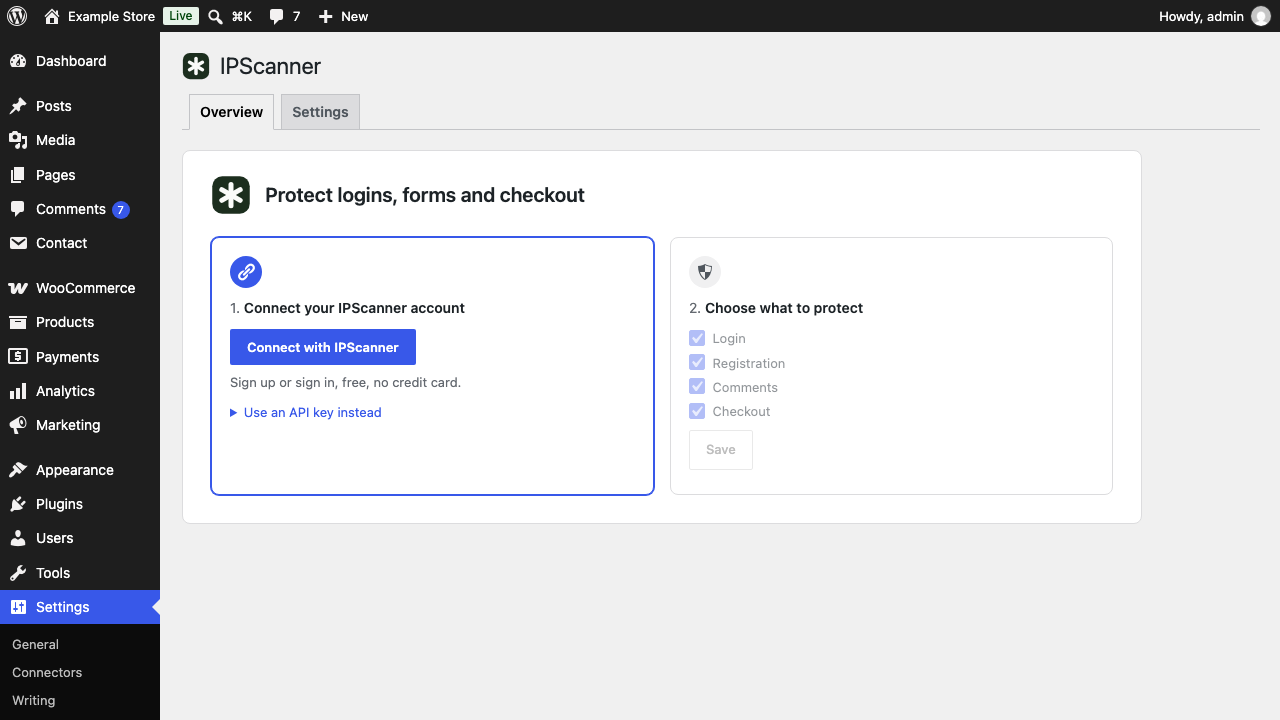
A CAPTCHA alternative with no puzzle. IPScanner checks each visitor on the server and blocks bots before they reach your forms.
What it stops
- Fake signups and spam registrations on WordPress and WooCommerce
- Comment spam and contact form spam
- Card-testing bots on WooCommerce checkout
- Login attacks from bots, Tor and proxies
- VPN and proxy traffic where you don’t want it
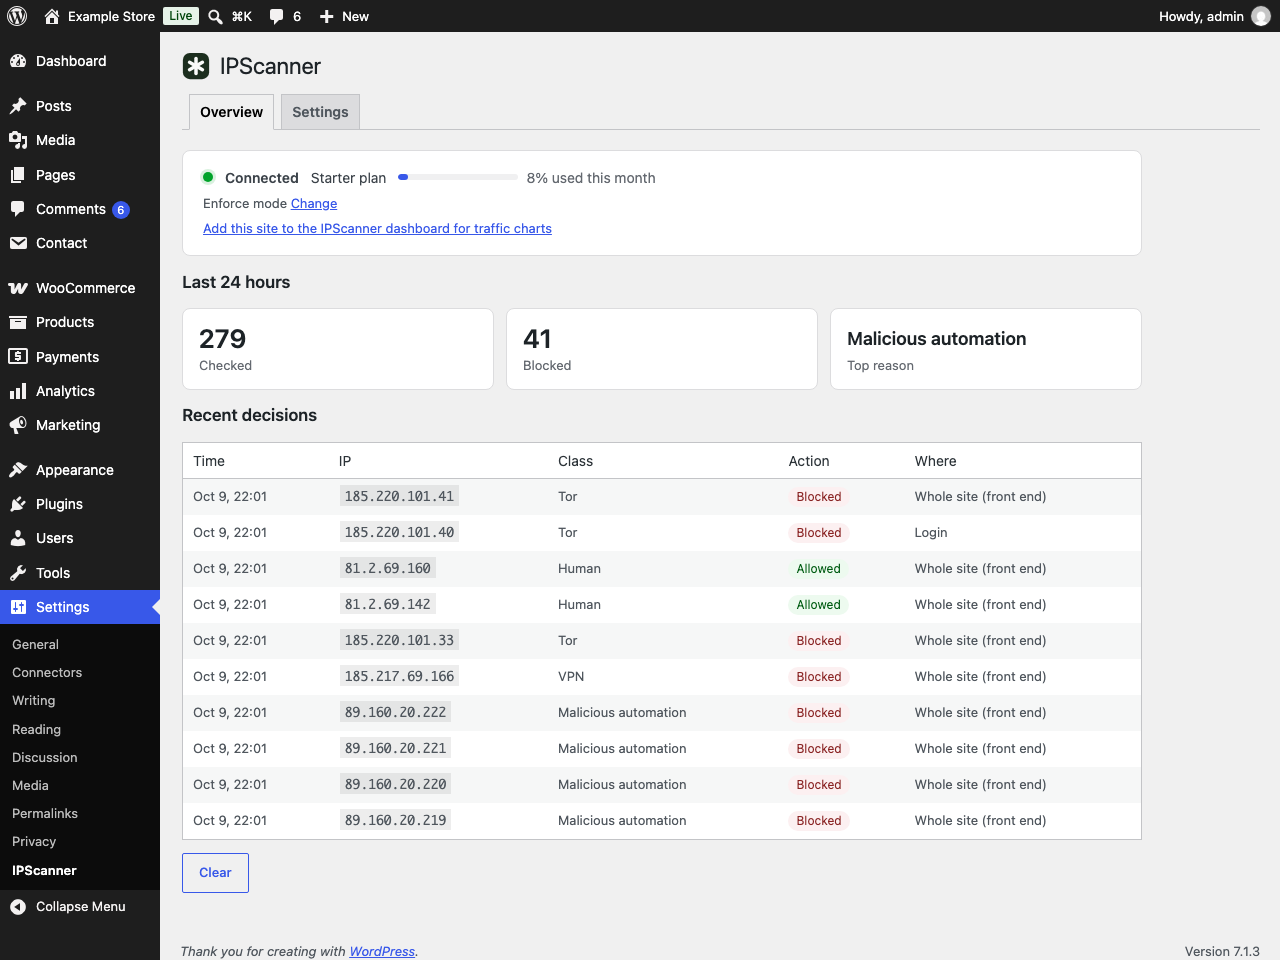
IPScanner checks each visitor with the IPScanner API and sorts them into one class: human, verified crawler, AI agent, malicious automation, Tor, VPN, proxy, hosting or privacy relay. You choose which classes to block and where.
Where it checks
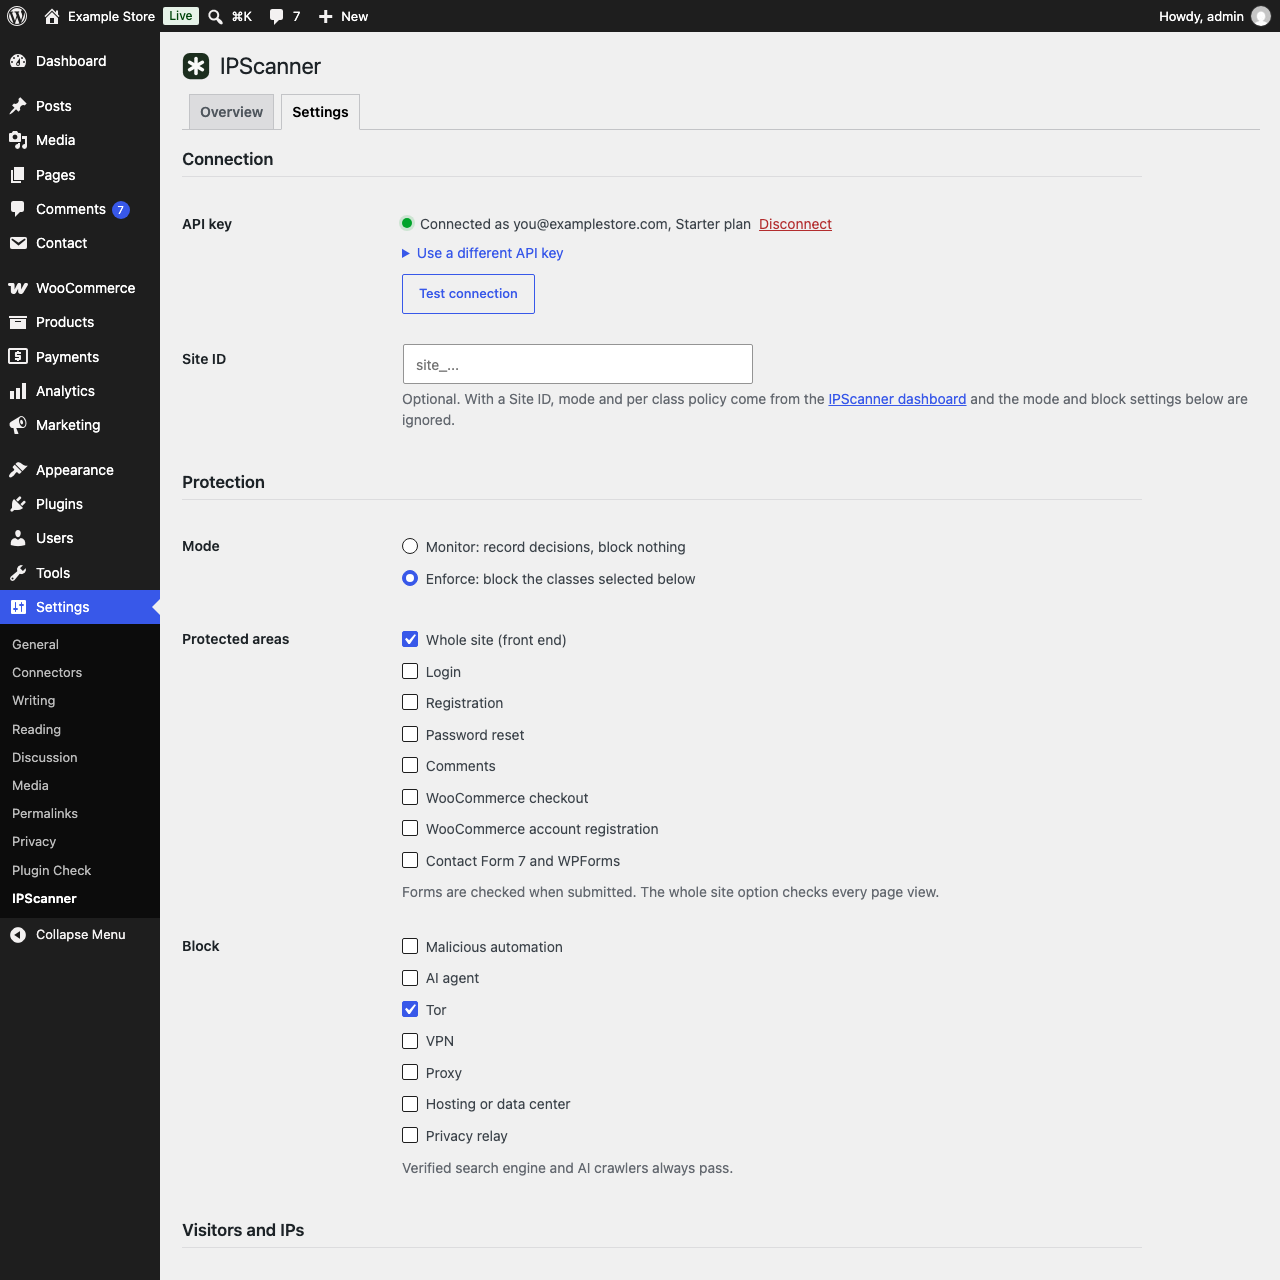
- Login, registration and password reset
- Comments
- WooCommerce checkout (classic and block checkout) and account registration
- Contact Form 7 and WPForms submissions
- The whole front end (optional, off by default)
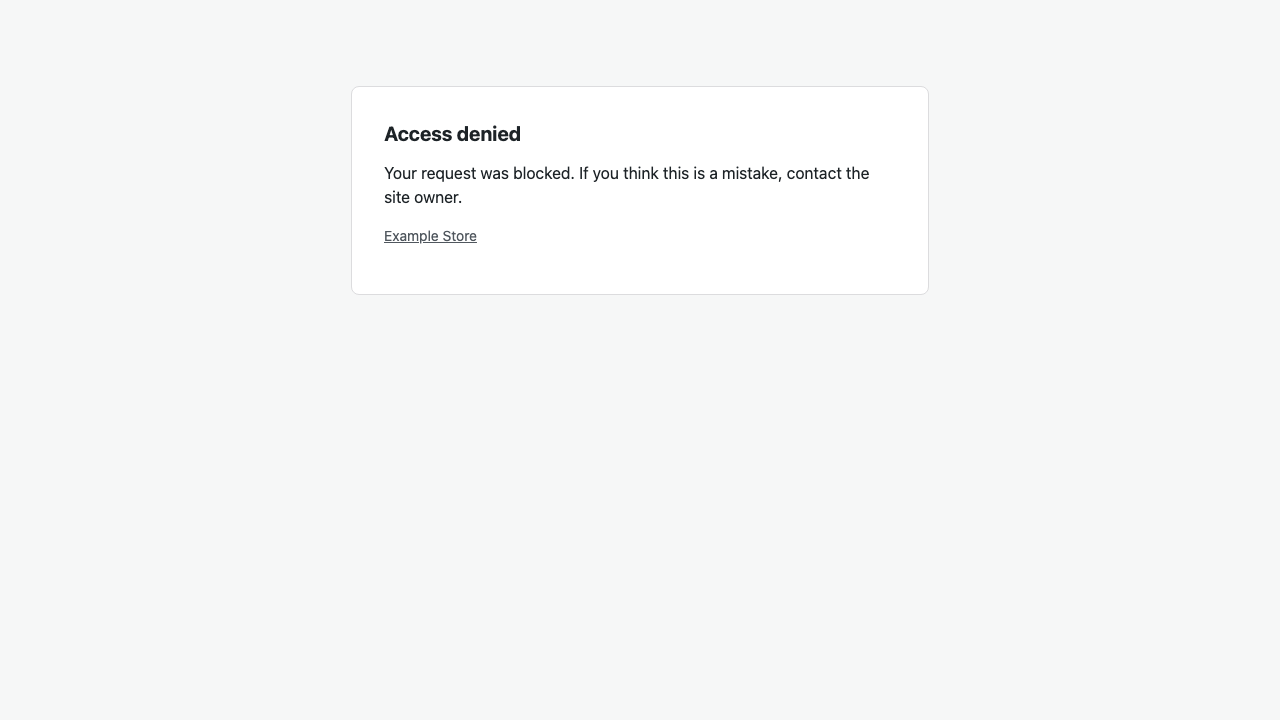
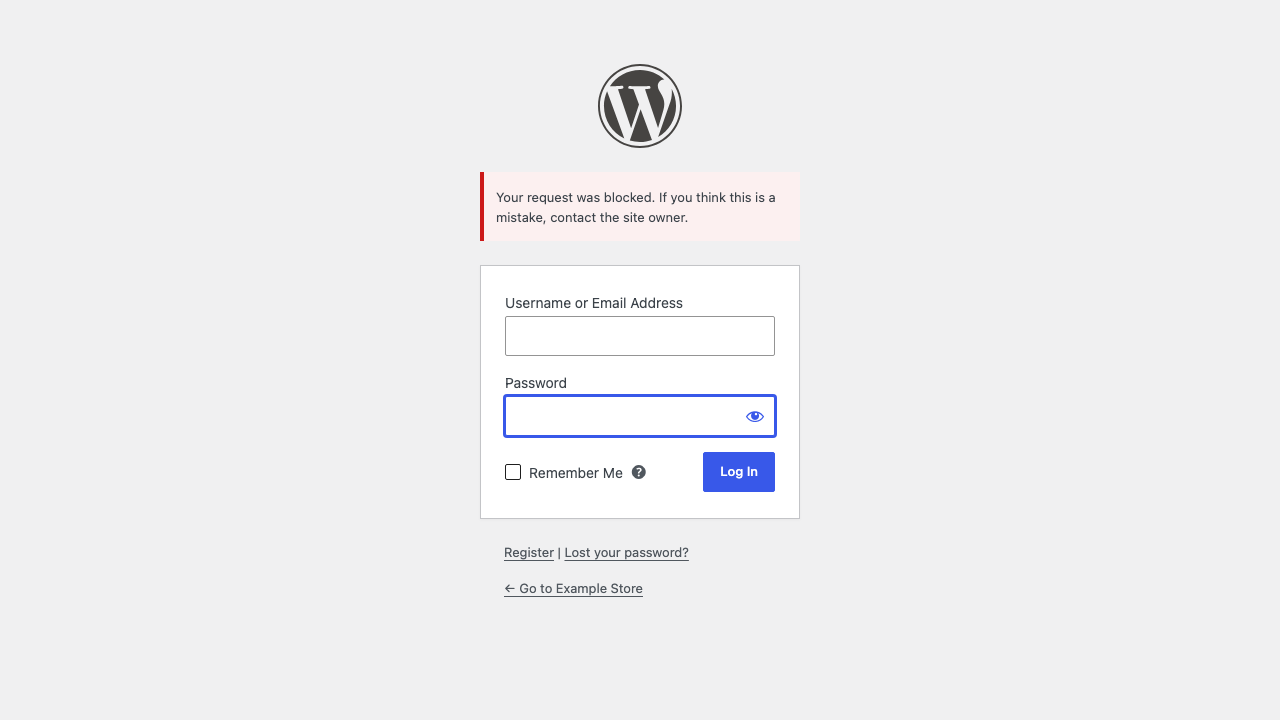
Forms get an error message. Pages get a short 403 page.
How it decides
- Monitor mode records decisions and blocks nothing. Start here.
- Enforce mode blocks the classes you select. The default is malicious automation only.
- With a Site ID from the IPScanner dashboard, mode and per class policy (allow, flag, block) come from the dashboard, and changes apply within 30 seconds.
- Verified search engine and AI crawlers always pass.
- Administrators and the IP addresses or ranges you list are never blocked.
What it costs
Each new visitor check uses 2 requests from your IPScanner allowance. A visitor is checked at most once every 10 minutes. Static files, the admin area, AJAX, cron and REST requests are never checked.
Fail open
If the API is slow (1.5 second timeout by default), unreachable or out of allowance, visitors are allowed and checks pause for a short while.
Behind a proxy
Choose Cloudflare or X-Forwarded-For under Visitor IP. Proxy headers are only read from trusted proxy addresses (Cloudflare ranges are built in), so visitors cannot fake their address.
External services
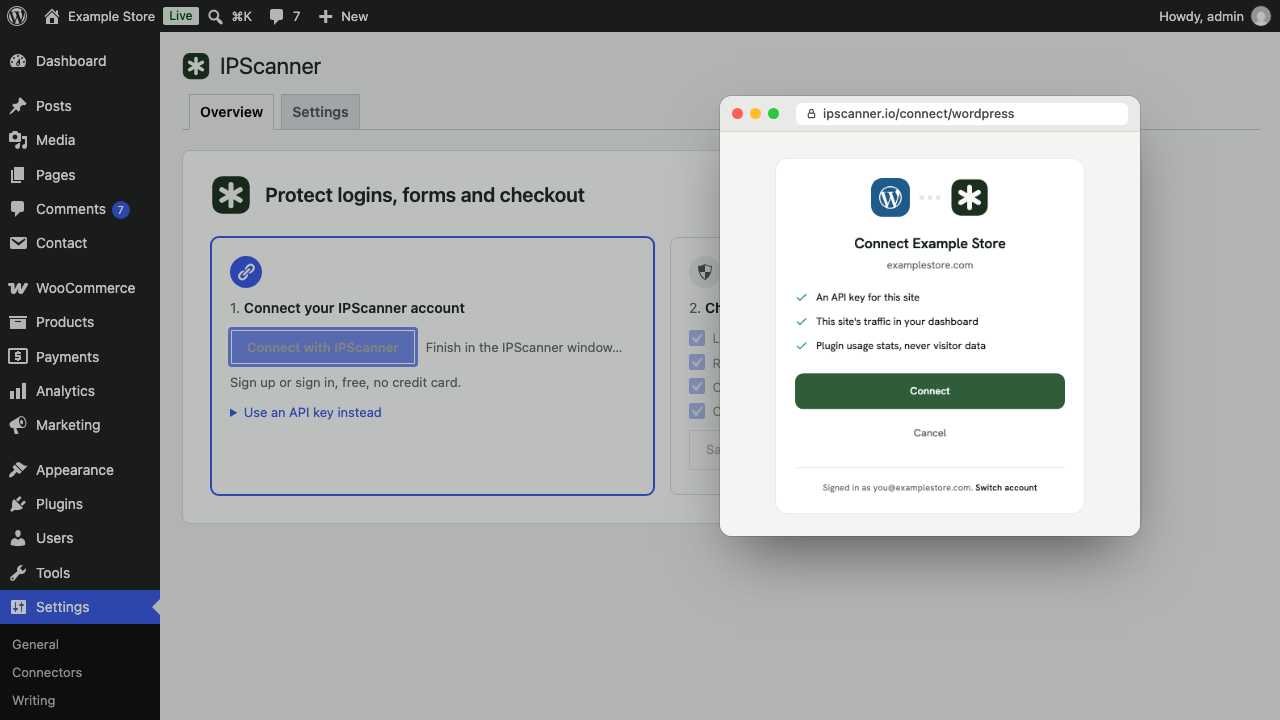
This plugin connects to the IPScanner API at https://ipscanner.io, run by IPScanner. It is required for the plugin to work.
- When a protected form is submitted, or a page is viewed with whole site protection on, the plugin sends the visitor’s IP address, user agent and these request headers: Accept, Accept-Language, Accept-Encoding, Sec-CH-UA and Sec-Fetch headers. It also sends a random request ID and your Site ID when one is set. Endpoint:
POST /v1/edge/check. Results are cached on your site for 10 minutes per visitor. - With a Site ID set, the plugin reads the site’s policy (no visitor data) at most every 30 seconds. Endpoint:
GET /v1/sites/{site}/policy. - When an administrator opens Settings > IPScanner (at most every 5 minutes) or clicks Test connection, the plugin reads the plan and usage of the API key (no visitor data). Endpoint:
GET /v1/usage/summary.
Nothing is sent before an API key is saved.
Terms of service: https://ipscanner.io/terms
Privacy policy: https://ipscanner.io/privacy
Source code: https://github.com/ipscanner/ipscanner-wordpress
Details
Related plugins
Plugins that also contain the tag anti-spam
Akismet Anti-spam: Spam Protection
Antispam Bee
CF7 Apps – Honeypot, Database, Redirection, Webhook, and Addons for Contact Form 7
WP Armour – Honeypot Anti Spam
CloudSecure WP Security
Gravity Forms Zero Spam

About
Plugin for that tries to help you find the WordPress plugin you are looking for.
| Please enjoy an image of Crush (this awesome turtle) and have a lovely day! |  |
We do not own any plugin listed on this site and do not work for or work with WordPress.com or it's associated companies. We simply provide a searchable list of the available WordPress plugins.