


PrivacyScrubber ZTDS Guard
PrivacyScrubber ZTDS Guard (Plane 6 of the PrivacyScrubber ecosystem) enforces the Zero-Trust Data Sanitization (ZTDS™ RFC v1.0) protocol on WordPress contact, patient intake, legal consultation, and financial onboarding forms.
When a visitor submits a form on your WordPress site, sensitive data frequently flows into third-party webhooks (Zapier, Make), CRM systems (HubSpot, Salesforce), Slack notifications, and AI triage bots (OpenAI, Anthropic Claude). PrivacyScrubber ZTDS Guard intercepts the form submission inside the visitor’s browser RAM (<0.4ms) during the DOM capture phase—before fetch() or XMLHttpRequest sends data over the network.
Dual-Envelope Architecture
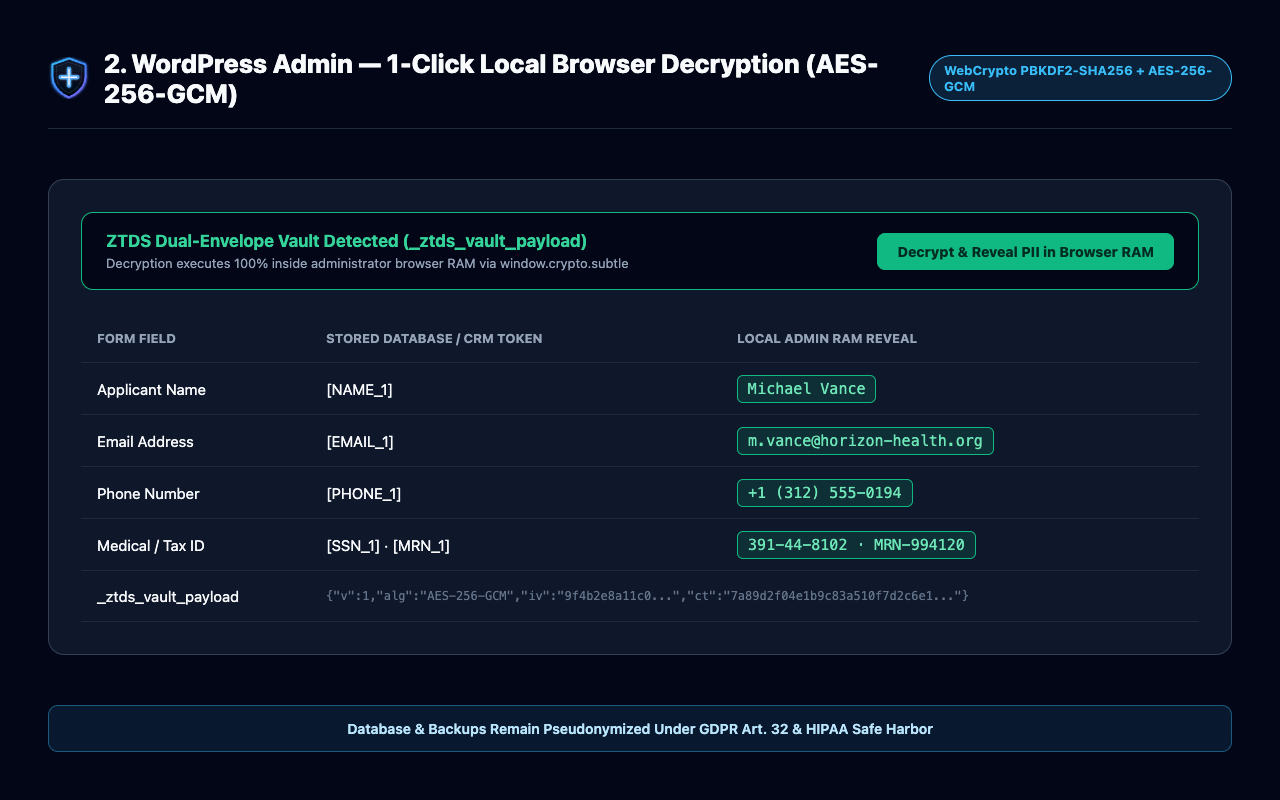
- Public Envelope (Sanitized Form Fields): Sensitive identifiers (Names, Phone Numbers, Emails, Payment Cards, SSN/National IDs, IBANs, Medical Record Numbers, Tax IDs) are replaced in-memory with deterministic tokens such as
[NAME_1],[PHONE_1],[EMAIL_1], and[SSN_1]. Downstream CRMs, email notifications, and AI triage agents process the inquiry with zero exposure to raw PII/PHI. - Private Vault Envelope (
_ztds_vault_payload): The original cleartext mapping is encrypted inside the visitor’s browser using native WebCrypto (AES-256-GCM+PBKDF2-SHA256) and attached as a sealed hidden payload. Authorized administrators can decrypt and reveal original entries in 1 click inside the WordPress Admin dashboard using their local browser key.
Supported Form Builders
- Contact Form 7 (
form.wpcf7-form) - WPForms (
form.wpforms-form) - Elementor Forms (
form.elementor-form) - Gravity Forms (
.gform_wrapper form,form[id^="gform_"]) - Fluent Forms (
form.fluentform) - Custom HTML / AJAX Forms (via
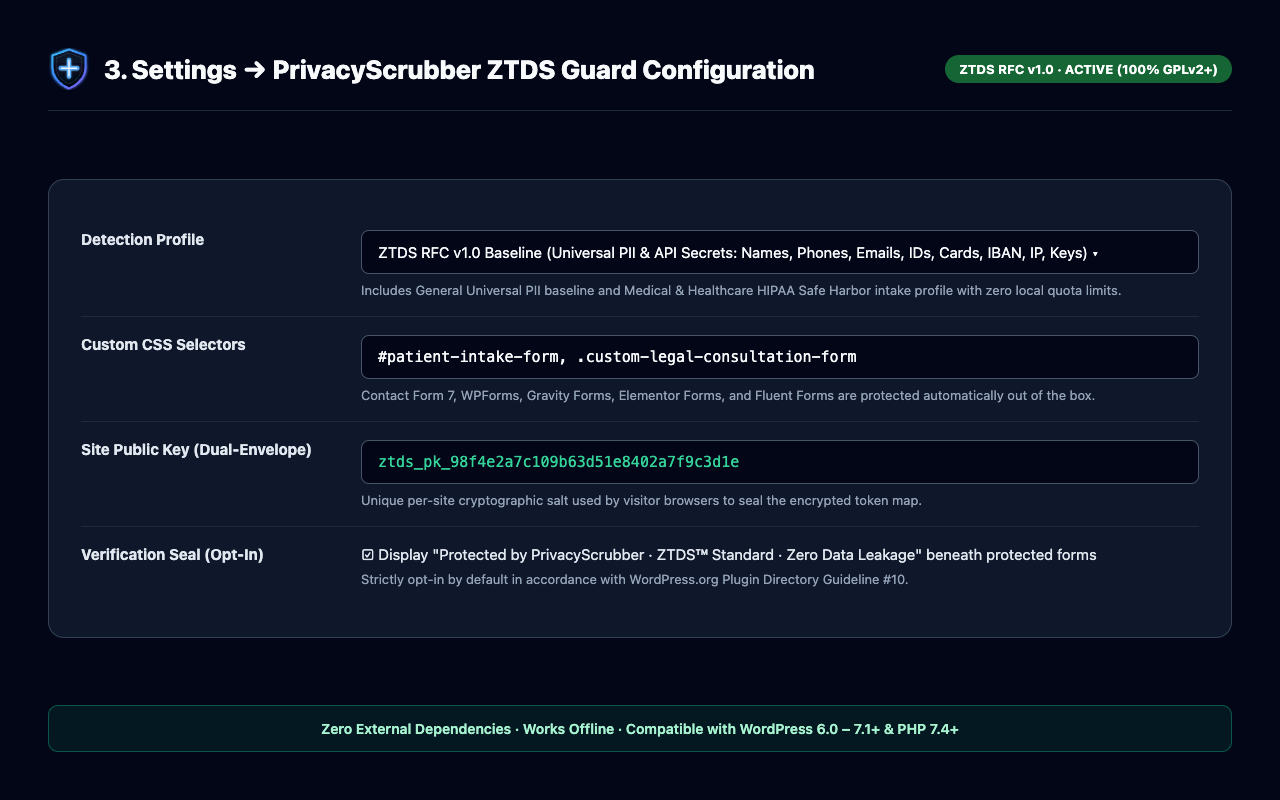
data-ztds="true"or custom CSS selectors in Settings)
Key Architectural Guarantees
- Zero External Network Egress: 100% of detection, tokenization, and encryption executes locally in the visitor’s browser (
window.crypto.subtle). Zero bytes of form content are ever transmitted to PrivacyScrubber or third-party servers. - Fail-Open Business Continuity: If a legacy browser lacks WebCrypto support or encounters a custom DOM exception, the interceptor gracefully bypasses tokenization so your business never loses an inbound lead.
- Statutory Risk Minimization: Technical & Organizational Measure (TOM) supporting GDPR Article 32 pseudonymization, HIPAA Safe Harbor (45 CFR § 164.514(b)), and PCI-DSS v4.0 intake hygiene.
External Services & Privacy Disclosure
This plugin executes 100% locally in the visitor’s browser and does not transmit any form data, visitor PII, or telemetry to any external server. Optional verification badge links to https://privacyscrubber.com/integrations/wordpress/ and https://ztds.ai/ are strictly controlled by the site administrator under Settings -> PrivacyScrubber ZTDS.
Details

Related plugins
Plugins that also contain the tag contact-form-7
ReCaptcha v2 for Contact Form 7

Contact Form 7 Captcha
Contact Form 7 – Dynamic Text Extension
Conditional Fields for Contact Form 7
Image CAPTCHA for Contact Form 7 and WPForms by HookAndHook (DSGVO/GDPR)

Database for Contact Form 7, WPforms, Elementor forms

About
Plugin for that tries to help you find the WordPress plugin you are looking for.
| Please enjoy an image of Crush (this awesome turtle) and have a lovely day! |  |
We do not own any plugin listed on this site and do not work for or work with WordPress.com or it's associated companies. We simply provide a searchable list of the available WordPress plugins.