

TibaCheck — Site Audit
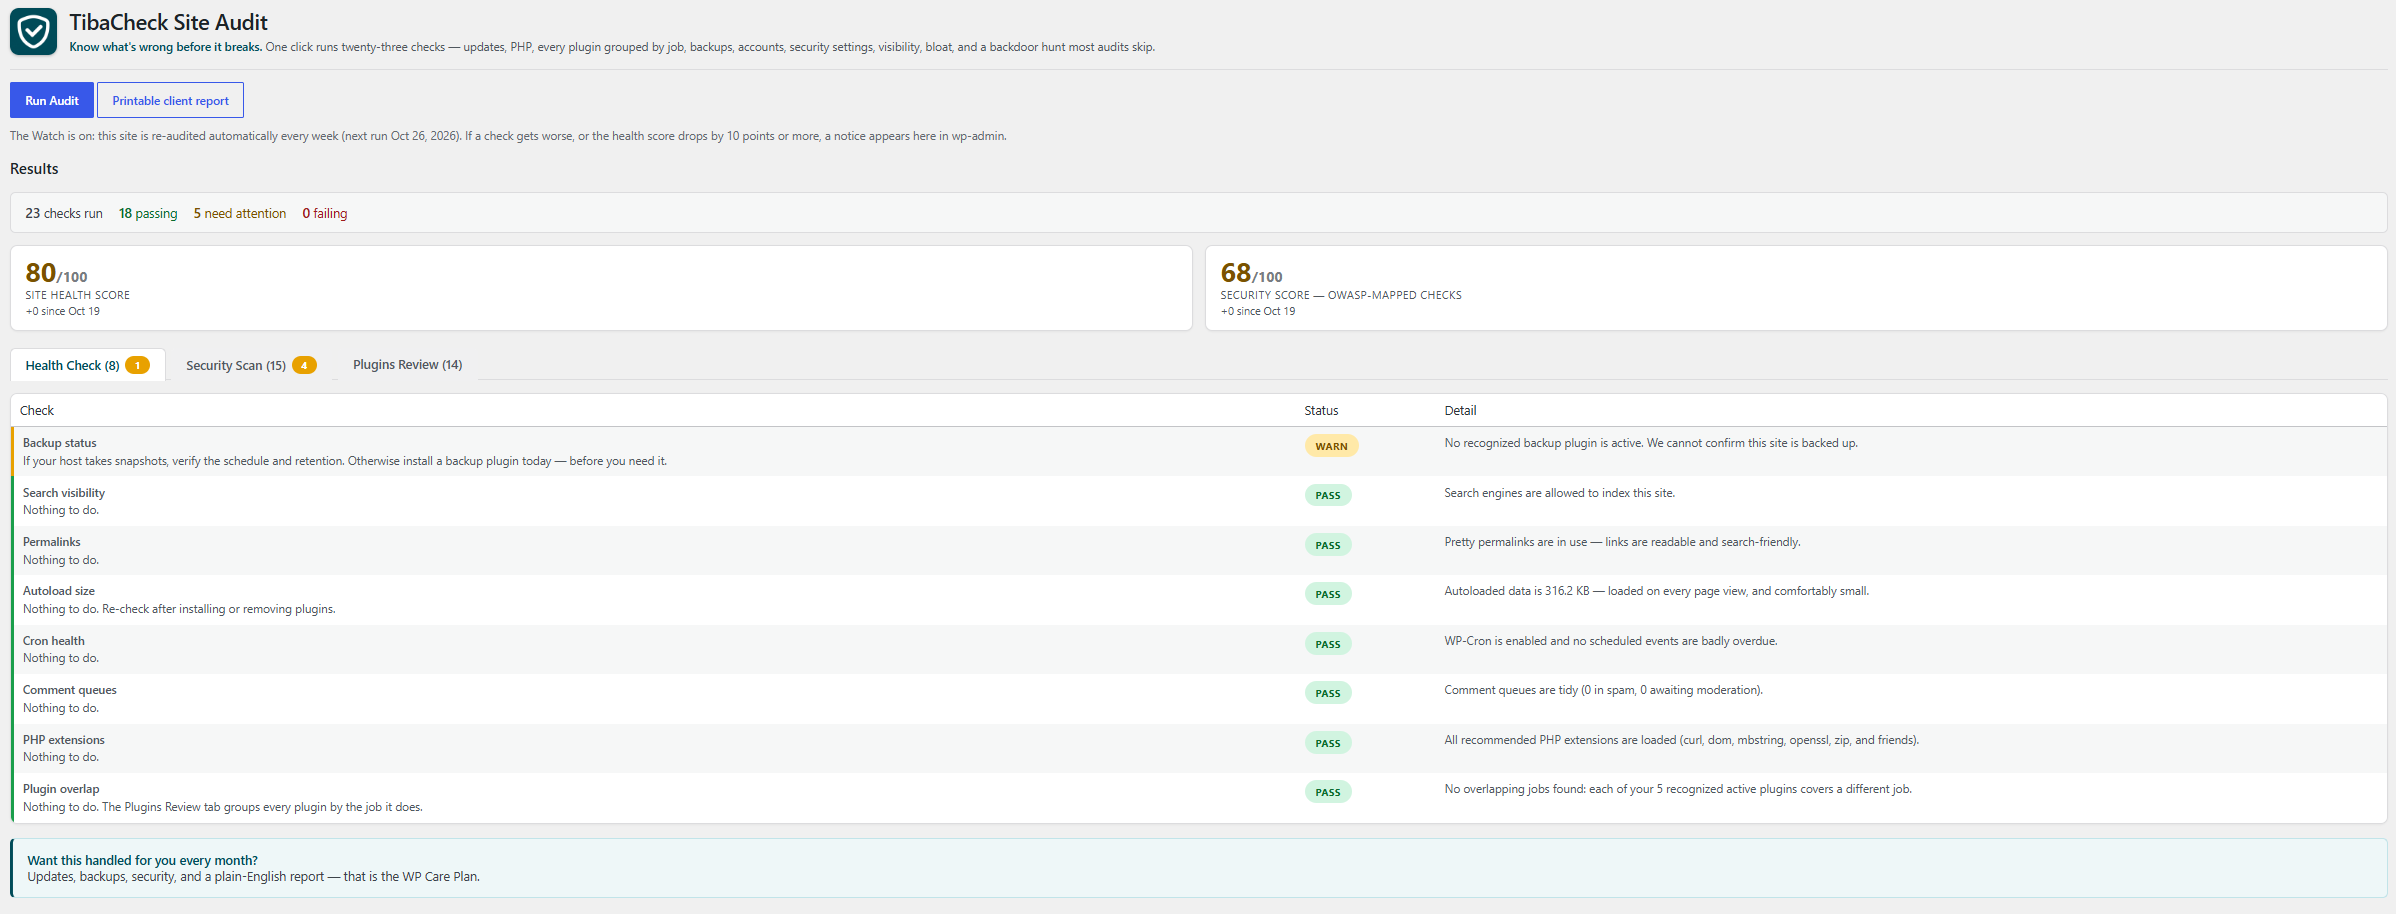
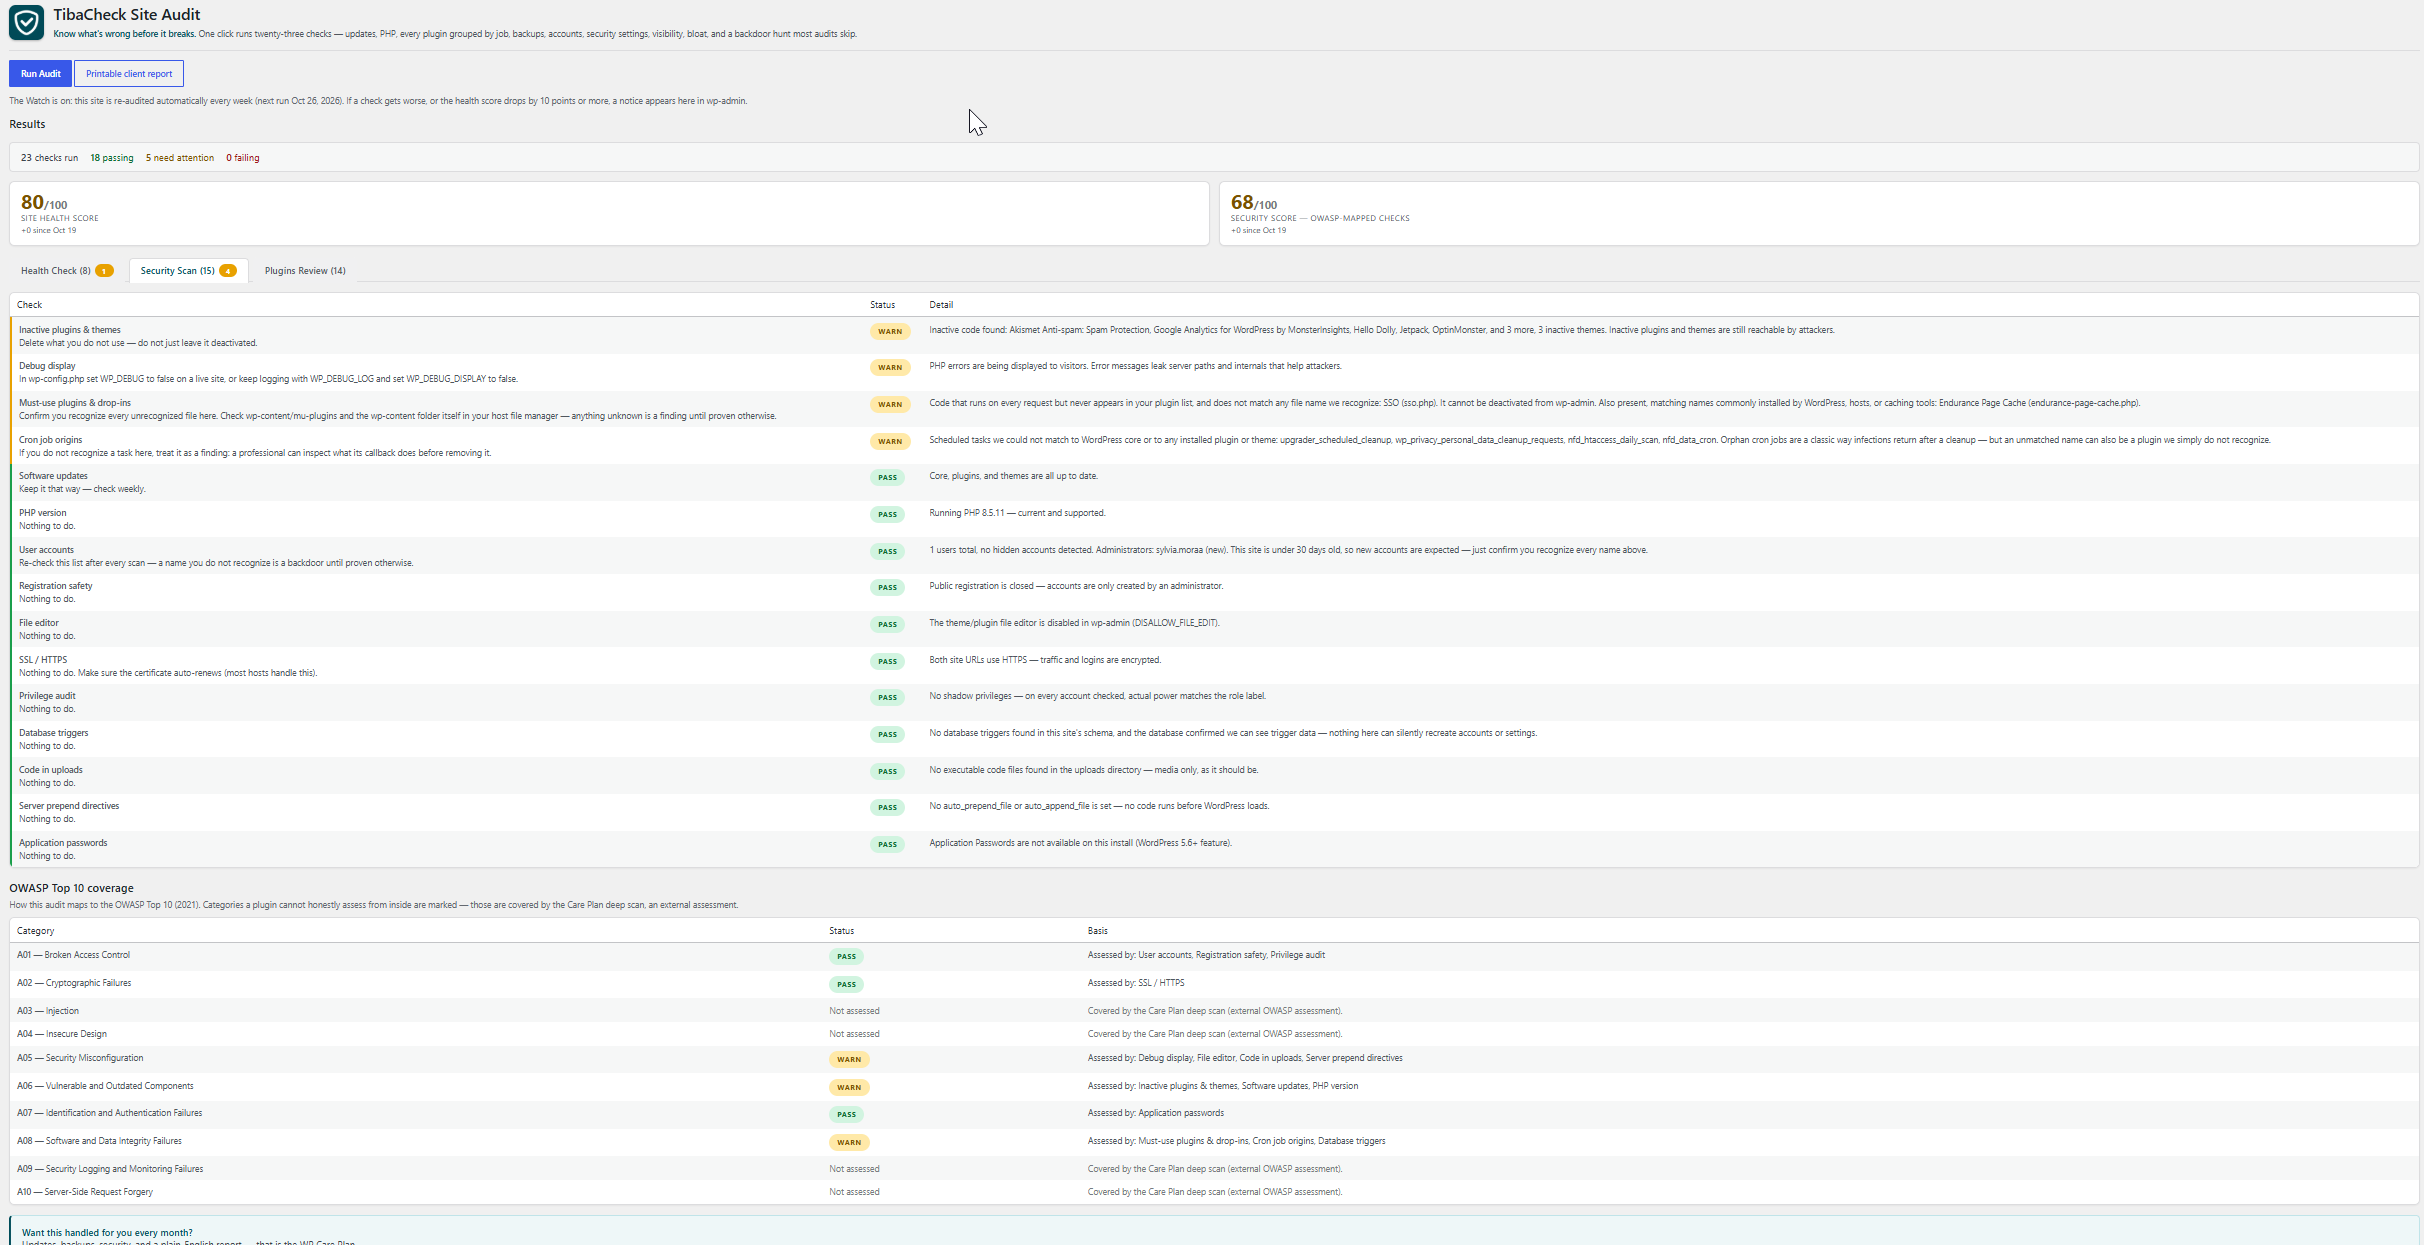
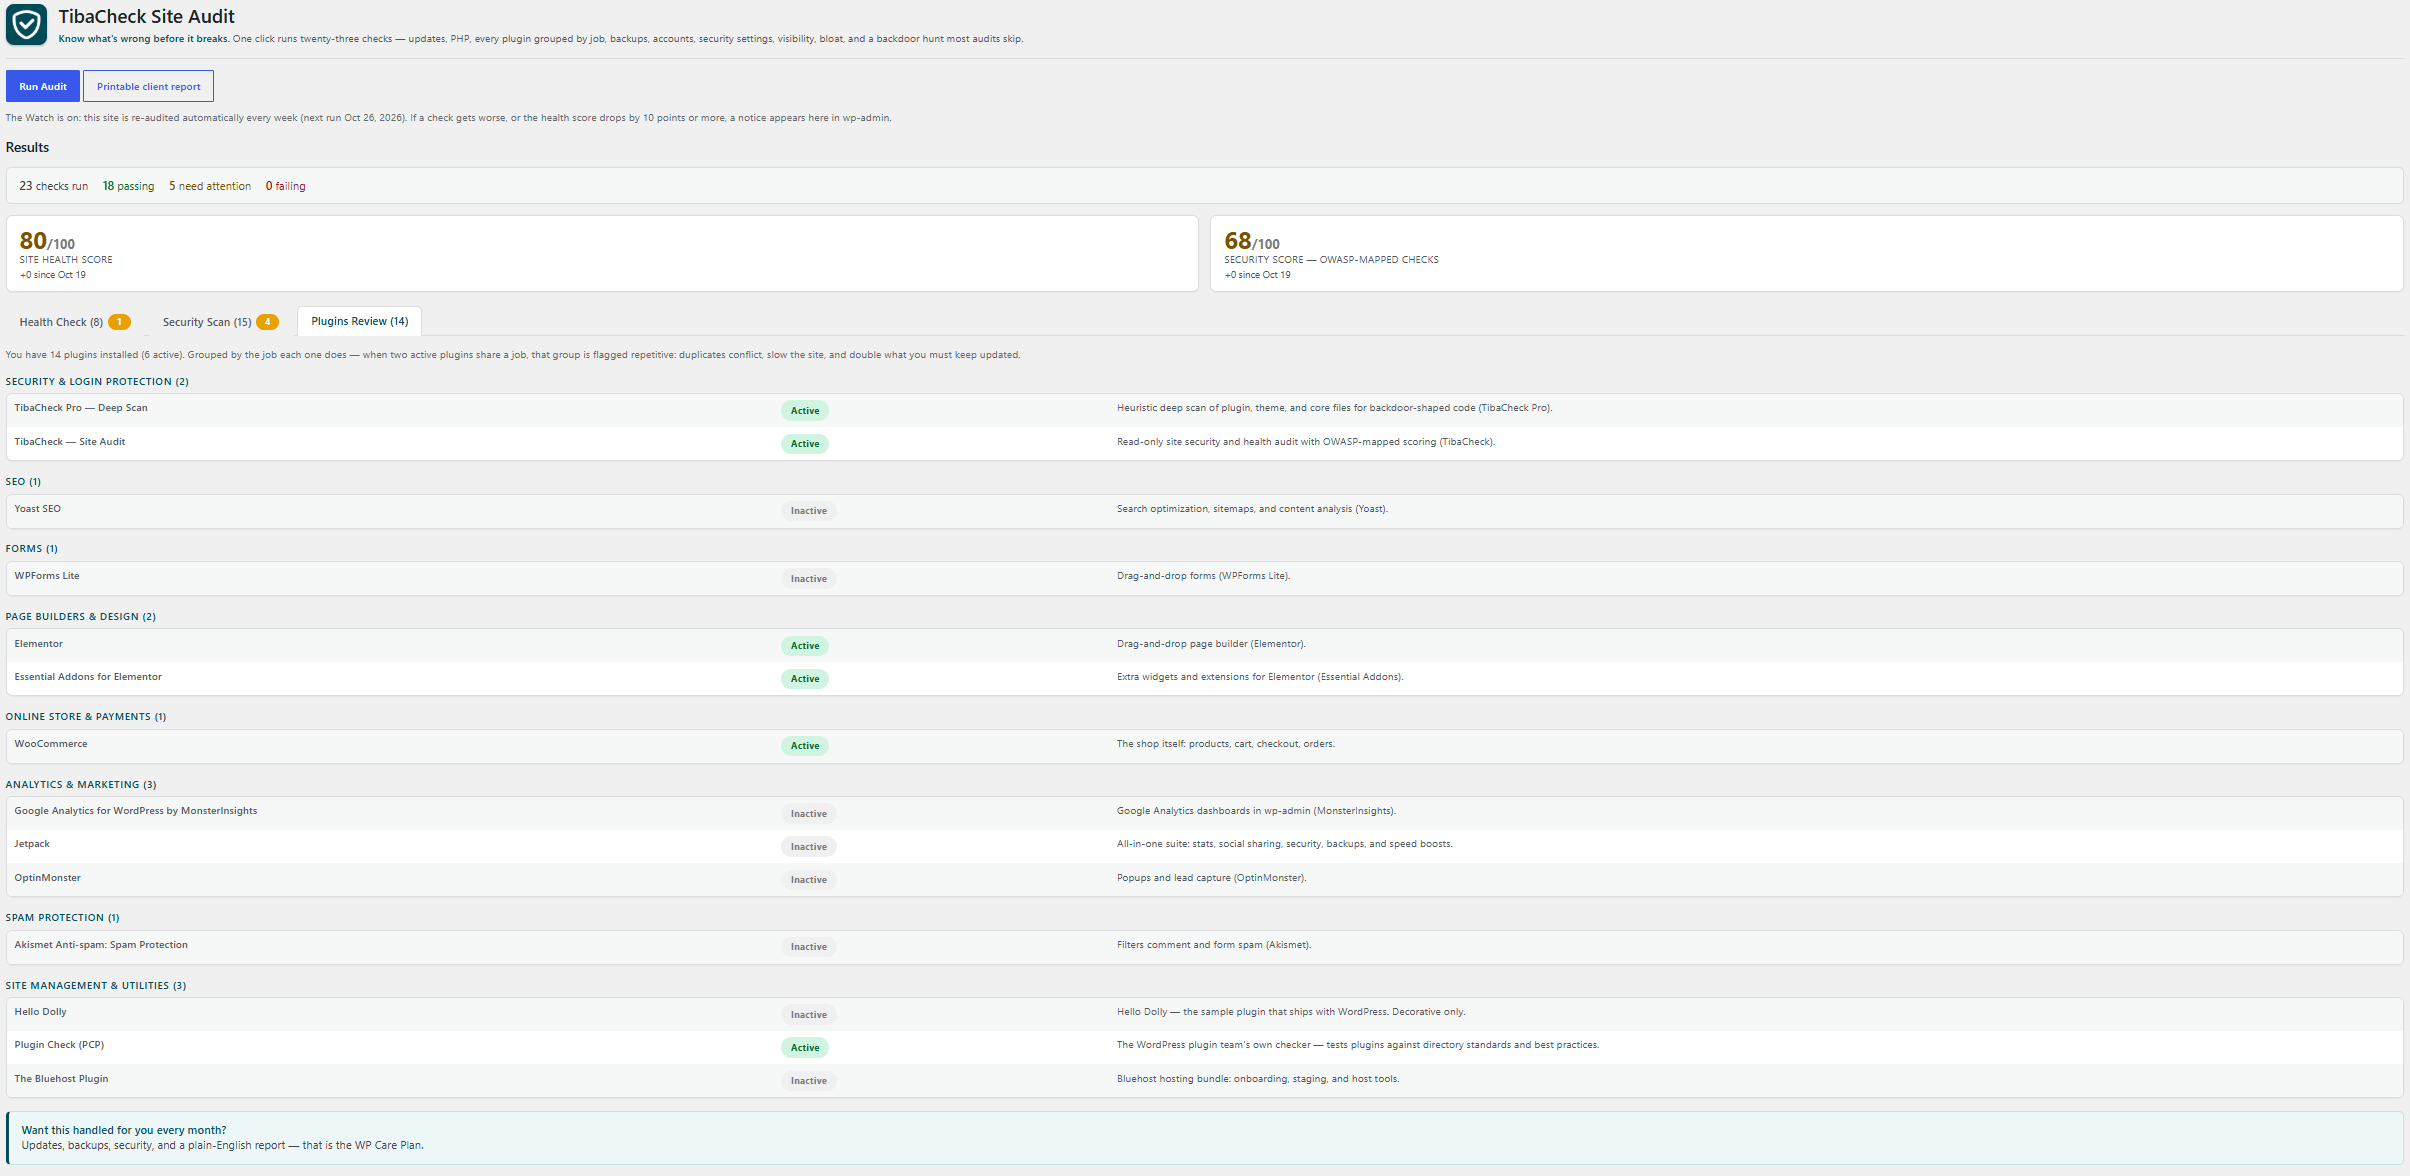
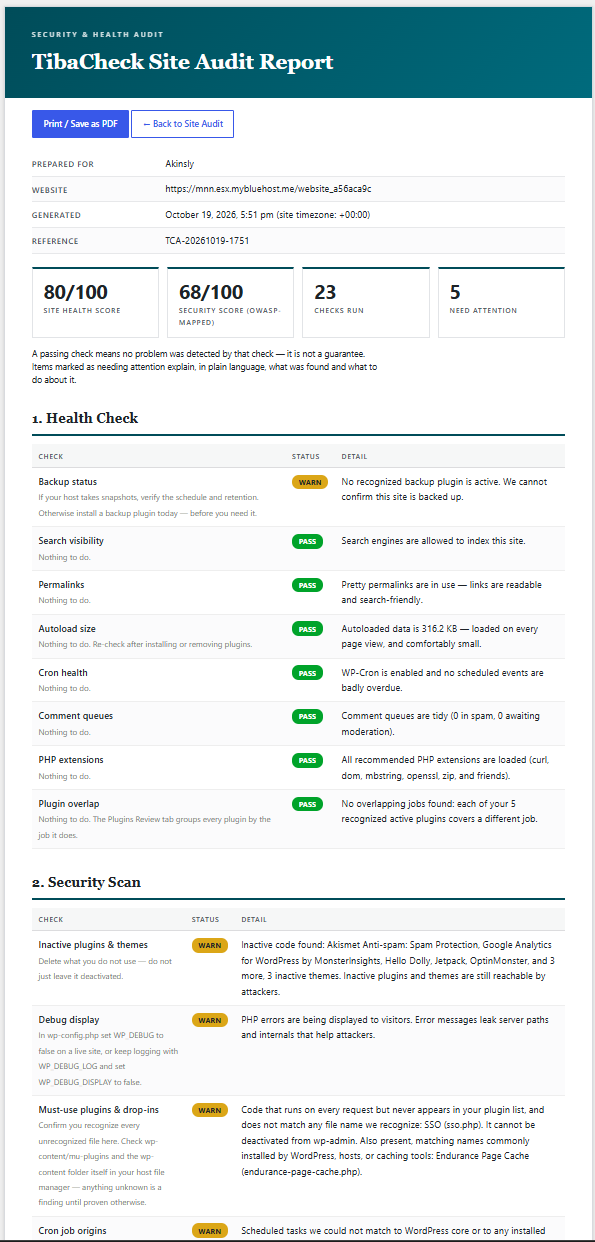
TibaCheck runs a read-only audit of your site’s configuration and shows you, in plain language, what needs attention. Every report leads with two scores — a Site Health Score and a Security Score built from checks mapped to the OWASP Top 10 (2021) — with a full OWASP coverage table showing what was assessed and what needs an external deep scan:
- Software updates — pending WordPress core, plugin, and theme updates (outdated software is the #1 way sites get hacked)
- PHP version — whether your PHP is supported, outdated, or end-of-life
- Inactive plugins & themes — unused code sitting on your site is a favorite hiding spot for malware
- Backup status — whether we can confirm this site is backed up at all
- User accounts — every administrator listed by name after each scan, plus a hidden-account test that catches backdoor users invisible to WordPress
- Registration safety — open registration paired with a powerful default role is an open door; we flag it
- File editor — whether the wp-admin theme/plugin editor (one stolen password away from code execution) is disabled
- Debug display — whether PHP errors are being shown to visitors, leaking server internals
- Search visibility — whether the site is accidentally telling Google to stay away
- SSL / HTTPS — whether both site URLs are actually configured for encrypted traffic
- Permalinks — whether links are readable and search-friendly, or the plain
?p=123default - Autoload size — how much data loads on every page view, with the biggest offenders named; bloat here is the #1 silent slowdown
- Cron health — whether scheduled tasks (updates, backups, posts) are actually firing, or silently stalled
- Comment queues — spam and unmoderated comments piling up in the database
- PHP extensions — whether the extensions WordPress relies on for updates, images, and encryption are present
Plus the Persistence Pack — the backdoor hunt most audits skip entirely:
- Privilege audit — accounts whose real power exceeds their role label (a “Subscriber” who can actually run the site)
- Must-use plugins & drop-ins — code that runs on every request but never appears in your plugin list, listed by name; files matching names commonly installed by WordPress, hosts, or caching tools are called out separately from names we cannot recognize
- Database triggers — triggers on account tables can silently recreate a deleted backdoor; we inspect the schema
- Cron job origins — scheduled tasks that trace to neither core nor any installed plugin or theme are how cleaned infections return
- Code in uploads — executable files inside the media folder, where only images and documents belong
- Server prepend directives — auto_prepend_file / auto_append_file run code before WordPress even loads; we show you if they’re set
- Application passwords — an inventory of the standing credentials that bypass your login screen, with the oldest one’s age
Every report also carries a Plugins Review section: every installed plugin grouped by the job it does — backups, security, SEO, speed, forms, builders, store, analytics, spam, media, email, languages, utilities — each with a one-line purpose and its active/inactive state. When two or more active plugins share a job, the group is flagged repetitive and a Plugin Overlap check warns: duplicates conflict, slow the site, and double what you must keep updated. Plugins we don’t recognize are listed honestly as “not yet categorized” — we never guess what a plugin does.
Every report can also be opened as a printable client report: a branded document with the score cards, every check and its detail, and the plugin and OWASP coverage summaries — ready to print or save as a PDF for a client. It is generated fresh when opened; the plugin stores no full report (only scores, statuses, and time).
The Watch keeps an eye on the site between visits: once a week, TibaCheck quietly re-runs the same read-only audit on its own (using WordPress’s built-in scheduler — no external calls, nothing phones home). If a check gets worse than the last audit, or the health score drops by 10 points or more, a notice appears in wp-admin naming what changed. A manual audit run answers the notice; improving checks never raise one, and each weekly run reconciles an unanswered notice — problems that recovered drop off it, problems still active stay on it. Deactivating the plugin stops the Watch and discards any pending notice (on a multisite network, deactivate on the site itself to clear that site’s Watch).
A note on honesty: TibaCheck does not claim to “scan for malware” the way signature scanners do — signatures miss modern, per-site malware, and a scanner runs inside the very environment an infection can hide from. What it does is audit the places malware must live, persist, and act: its hiding spots, its survival tricks, and the accounts it needs. Those it finds, it names.
More checks are on the roadmap: file permissions and deeper performance profiling.
TibaCheck never changes your site’s content or settings — it reports. The only thing it saves is its own last report (scores and statuses, in its own settings), any pending Watch change alert, and the time of the last automatic Watch run, so your next scan can show whether your scores are rising or falling. Fixing is up to you, or the care-plan team that handles it every month.
Details
Related plugins
Plugins that also contain the tag audit
Audit Trail
Sa11y, the accessibility quality assurance assistant | Accessibility Checker
BCC All Emails

BoltAudit – Plugin & Performance Analyzer

Content Audit

Post Author IP

About
Plugin for that tries to help you find the WordPress plugin you are looking for.
| Please enjoy an image of Crush (this awesome turtle) and have a lovely day! |  |
We do not own any plugin listed on this site and do not work for or work with WordPress.com or it's associated companies. We simply provide a searchable list of the available WordPress plugins.